Two forces are driving CBOM tools adoption simultaneously: regulatory pressure and the quantum threat.
India’s regulators have moved decisively. CERT-In’s Technical Guidelines make CBOM mandatory for critical applications, with defined minimum data elements for every cryptographic asset. RBI references these guidelines directly. Globally, NIST finalised its post-quantum cryptography standards in 2024 and has set 2030 as the deprecation date for quantum-vulnerable algorithms such as RSA and ECC, with full migration required by 2035. The EU Cyber Resilience Act also requires cryptographic component documentation for all digital products.
Behind the scenes, cybercriminals are not waiting for quantum hardware to arrive. They are capturing encrypted traffic today to decrypt it once capable systems come into existence. Financial records with long retention periods and long-lived signing keys are already at risk. The right CBOM tool will give you a precise map of what needs to migrate before the deadline forces a rushed response.
In this blog, our experts review the top 5 keeping an eye on the changing regulations and what the post-quantum era could look like.
A note on our ranking: CyberNX CBOM Solutions sit at the top of this list because we built it specifically for this problem. We have been transparent about its limitations alongside its strengths. We believe the features speak for themselves, but we encourage you to weigh every option here against your own requirements
Top 5 CBOM tools in 2025
The CBOM tooling market has matured quickly. The following CBOM tools list represent the leading options available today. Each has genuine strengths and limitations. The right choice depends on your infrastructure, regulatory obligations and internal capabilities.
| Capability | (CyberNX CBOM Solutions) | SandboxAQ AQtive Guard | IBM Quantum Safe Explorer | QCecuring CBOM | PQCA CBOMkit |
| Discovery scope | Code, network, containers, binaries | Network + AI (agentless) | Code + mainframe (z/OS, COBOL) | Network + certificates | Code + dependencies (CI/CD) |
| SBOM + CBOM together | ✅ Both on one platform | ❌ | ❌ | ❌ | ⚠️ SBOM integration only |
| CycloneDX output | ✅ Native | ❌ Proprietary | ❌ Proprietary | ✅ Native | ✅ Reference implementation |
| PQC readiness | ✅ Assessment + migration roadmap | ✅ HNDL risk scoring | ✅ Detailed migration paths | ✅ | ⚠️ Partial |
| Continuous monitoring | ✅ Re-scored on every change | ✅ | ❌ | ✅ | ❌ Point-in-time only |
| Automated remediation | ⚠️ Guidance + roadmap | ❌ Discovery only | ❌ | ✅ Auto cert rotation | ❌ |
| Regulatory mapping | ✅ CERT-In, SEBI, RBI, EU CRA, ISO 27001 | ⚠️ Partial | ✅ NIST | ✅ CRA, DORA, PCI DSS | ❌ |
| Deployment flexibility | ✅ SaaS, private cloud, on-prem (full parity) | ⚠️ Cloud-managed | ✅ | ✅ | ✅ Self-hosted |
1. CyberNX CBOM Solutions
CyberNX combines SBOM and CBOM and focuses specifically for regulated Indian enterprises with explicit mappings to CERT-In’s 21 required fields, SEBI’s 9 fields and RBI cyber security directions.
The CBOM module scans source code, binaries, containers and network traffic to discover every cryptographic asset across your environment. It catalogues algorithms, key lengths, modes, protocols and certificate details in a unified registry, flags deprecated or weak cryptography such as MD5, SHA-1, RSA-1024 and TLS 1.0/1.1, and assesses each asset against NIST post-quantum cryptography standards. Findings feed into a structured, phased migration roadmap rather than a flat list of alerts.
Why it stands out: It is the only solution in this comparison that covers SBOM and CBOM together on a single dashboard with one unified risk score. Inventories are rebuilt and re-scored on every change, not once a quarter. Its context-aware prioritisation combines CVSS, EPSS, reachability analysis and business criticality.
Deployment is available as SaaS, private cloud or on-premises with full feature parity across all three. For BFSI organisations that cannot route cryptographic data through third-party cloud environments, on-premises support is a genuine differentiator.
Limitations: Does not support mainframe environments. Automated one-click certificate rotation, available in some dedicated certificate lifecycle management platforms, is not a current feature. Organisations with significant z/OS or COBOL infrastructure will need a separate tool for that layer.
Best for: Indian regulated enterprises, BFSI organisations and security teams that need SBOM and CBOM together under one roof with specific compliance output and on-premises deployment.
2. SandboxAQ AQtive Guard
SandboxAQ, spun out of Alphabet in 2022, brings AI-driven cryptographic discovery to large-scale enterprise and government deployments. AQtive Guard uses machine learning to identify cryptographic usage patterns in network traffic without requiring agents. It combines this with code repository scanning and non-human identity discovery covering service accounts, API keys and machine certificates. Its quantum risk scoring is tied to “harvest now, decrypt later” threat timelines, making it one of the more sophisticated tools for modelling long-term risk.
Why it stands out: No other tool on this list matches AQtive Guard at the scale of 100,000 or more endpoints. Its AI models find cryptographic usage that rule-based scanners miss, particularly in complex network environments. Government agency validation through DoD partnerships adds credibility for defence-adjacent organisations.
Limitations: AQtive Guard is a discovery tool only. It does not remediate findings. Output is in a proprietary format rather than native CycloneDX, which creates integration work for teams that need standard CBOM artifacts. Enterprise pricing typically starts in the six-figure range annually and significant professional services are required for deployment. The AI models also need a training period to produce accurate results in custom environments.
Best for: Very large enterprises and government agencies that need AI-powered cryptographic discovery at massive scale and have a separate programme for remediation.
3. IBM Quantum Safe Explorer
IBM Quantum Safe Explorer (QSE) is part of IBM’s broader Quantum Safe portfolio. It is the only tool in this comparison with deep mainframe support, covering z/OS ICSF, RACF key rings and COBOL codebases. For financial services organisations with legacy mainframe infrastructure, this is often the deciding factor. QSE performs static code analysis across Java, C/C++, Python and COBOL, identifies cryptographic API usage at the source level and produces migration planning outputs with specific algorithm replacement recommendations.
Why it stands out: If your organisation runs COBOL or z/OS, no other tool in this list addresses that environment. IBM’s migration planning outputs are among the most detailed available, giving teams concrete algorithm replacement paths rather than generic risk scores.
Limitations: QSE is heavily IBM-ecosystem focused. Organisations without IBM infrastructure will find limited value. Network-level discovery is minimal compared to other tools on this list. Reporting is in a proprietary format and complex deployments typically require an IBM consulting engagement.
Best for: Financial services and enterprises running significant mainframe infrastructure on z/OS, CICS and COBOL applications.
4. QCecuring CBOM
QCecuring’s CBOM capability is built directly into its certificate lifecycle management (CLM) platform. Rather than operating as a standalone discovery product, it extends CLM with cryptographic inventory and generates standard CycloneDX CBOMs. The platform discovers certificates and keys across hybrid infrastructure including on-premises, cloud and Kubernetes environments, scores each against PQC readiness standards and-uniquely among the tools on this list-can trigger automated certificate rotation directly from CBOM findings.
Why it stands out: QCecuring is the only platform here that discovers weak cryptography and can fix it automatically through integrated certificate lifecycle management. CycloneDX output is native, not an afterthought. For organisations already evaluating CLM solutions, this combination reduces the number of tools in their stack.
Limitations: The platform’s strength is in certificates and TLS. Code-level cryptographic analysis is shallower than dedicated scanning tools. It has no SBOM capability and no India-specific regulatory mapping for CERT-In or RBI. As a newer and smaller vendor, the integration ecosystem is more limited than established players.
Best for: Organisations that want cryptographic discovery integrated with automated certificate lifecycle management in a single product, particularly where reducing tool sprawl is a priority.
5. PQCA CBOMkit (open source)
CBOMkit is an open-source project developed under the Post-Quantum Cryptography Alliance (PQCA), a Linux Foundation initiative. It is a reference implementation for CycloneDX CBOM generation, designed from the ground up for integration into CI/CD pipelines. CBOMkit scans Java and Python libraries for cryptographic dependencies, identifies cryptographic algorithm usage in compiled binaries and integrates cleanly with established SBOM tools such as Syft and Trivy.
Why it stands out: CBOMkit is free, fully auditable and governed by the Linux Foundation. For DevSecOps teams that want CBOM generation baked into every build, it is the most pipeline-native option available. Its plugin architecture allows extension for custom scanners and its CycloneDX output is the reference implementation for the standard itself.
Limitations: CBOMkit has no network-level discovery capability. It offers no GUI, no compliance dashboards and no enterprise support beyond the community. There is no remediation function and the vulnerability database is smaller than commercial alternatives. For regulated enterprises that need multi-source discovery, compliance-mapped reporting and ongoing monitoring, CBOMkit alone is insufficient.
Best for: Engineering teams with strong DevSecOps practices that want CBOM generation integrated into CI/CD pipelines, or organisations evaluating the CBOM standard before committing to a commercial tool.

Choosing the right tool is only the first step. If you are starting from scratch, our step-by-step guide on how to build a CBOM walks you through scoping, scanning, structuring and maintaining your cryptographic inventory from day one.
5 things to look for in CBOM tools
Evaluate CBOM tools list against the following criteria:
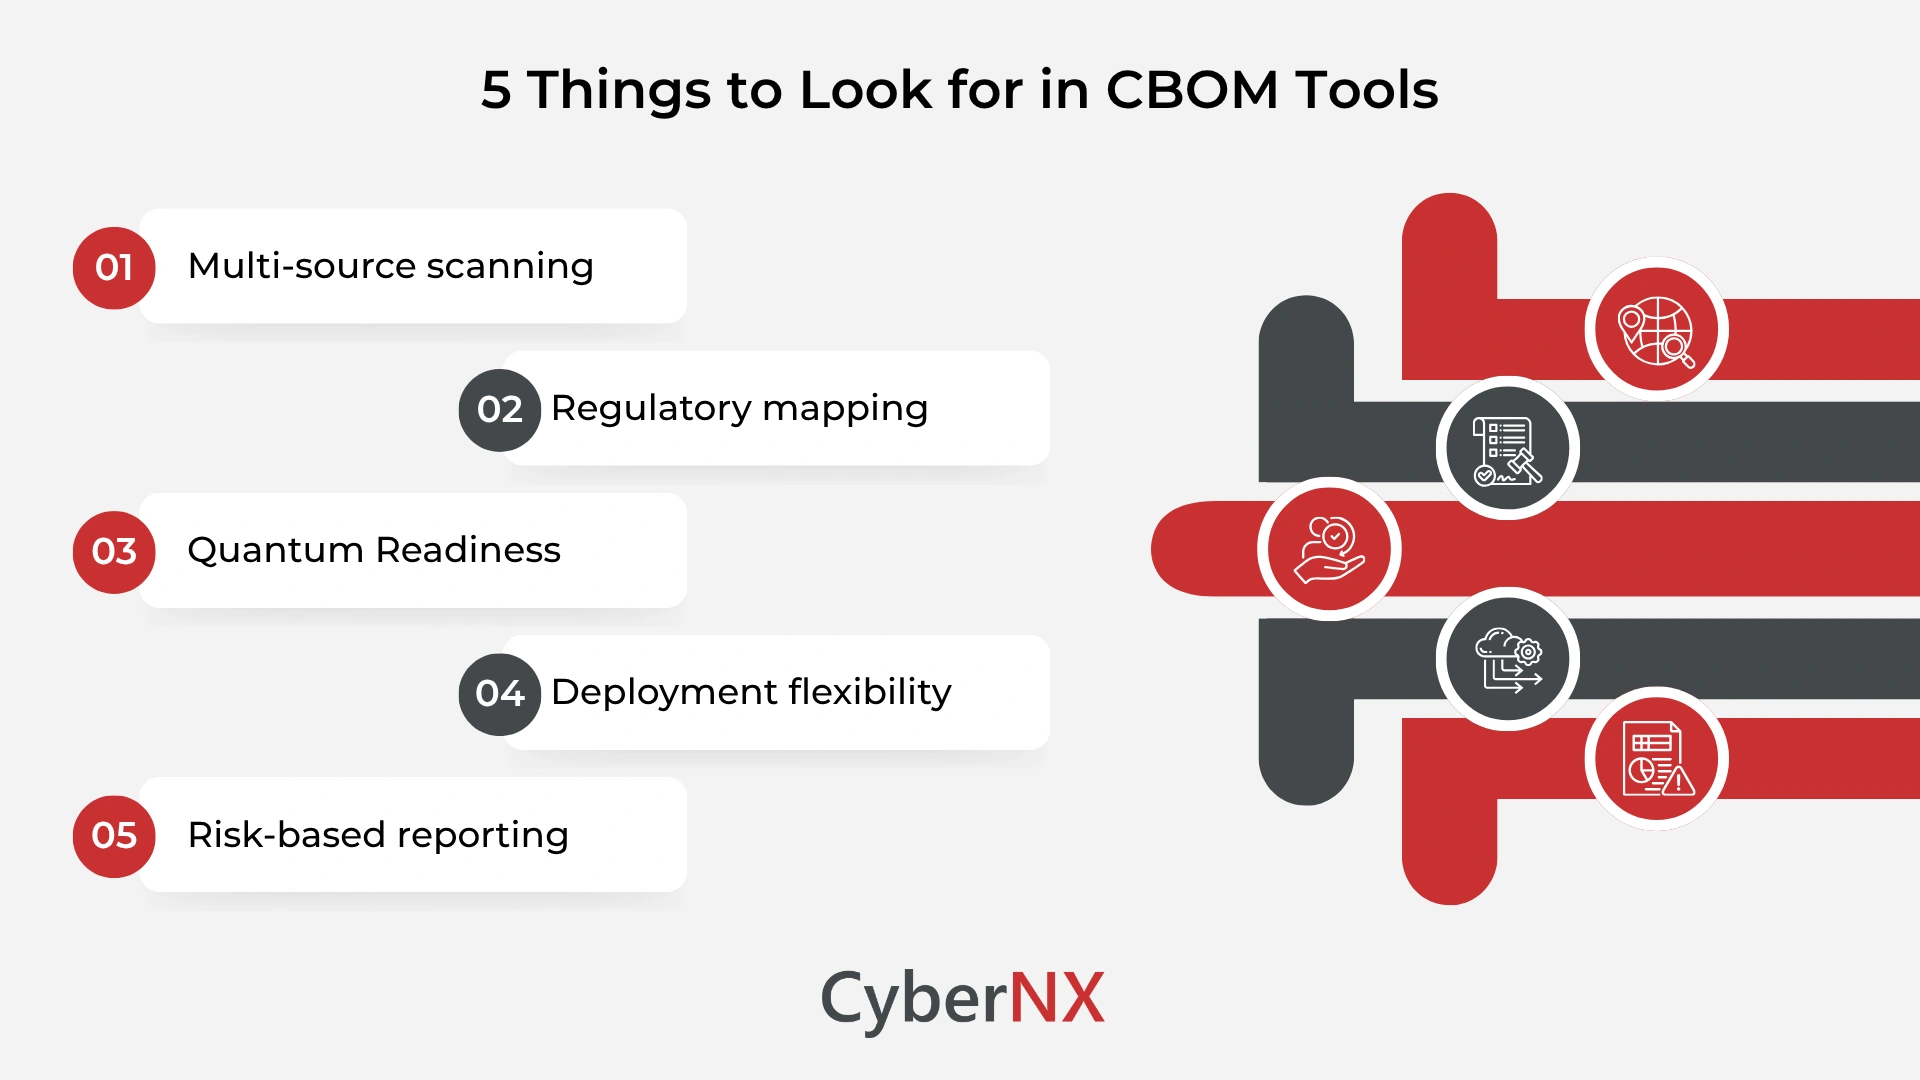
Multi-source scanning
A single scan type creates blind spots. Good CBOM tools combine network scanning, code repository analysis, artifact scanning and HSM/KMS integration to build a complete, de-duplicated picture.
Regulatory mapping
Look for platforms that map findings directly to RBI, CERT-In, NIST and EU CRA frameworks. This cuts audit preparation time and generates regulator-ready evidence packs without manual effort.
Post-quantum readiness tracking
The right tools detect quantum-vulnerable algorithms, track adoption of NIST-approved standards like ML-KEM and ML-DSA and generate migration roadmaps prioritised by quantum risk exposure.
Deployment flexibility
BFSI and regulated sectors often cannot route cryptographic data through third-party cloud environments. On-premise and air-gapped deployment support is non-negotiable for many regulated entities.
Risk-based reporting
A flat CSV of algorithms is not actionable. Look for platforms that prioritise findings by exploitability and business impact – the way a penetration testing report does, not a raw data dump.
Before you evaluate any tool, it helps to know where your organisation currently stands. We have put together a 12-question CBOM checklist that gives you an honest baseline of your cryptographic readiness – work through it first and the tool comparison below will be far more useful.
Conclusion
The right CBOM tools give your security and compliance teams a continuously updated map of your cryptographic estate. Something that holds up under audit and supports a structured post-quantum migration.
CyberNX’s CBOM Solutions are built for this challenge. It combines multi-source scanning across network, code, artifact and HSM/KMS environments, maps findings to RBI, CERT-In and NIST frameworks and supports on-premise deployment for BFSI and regulated sectors. If you are looking for CBOM tools list for your organisation, speak with our team today and see how our solution can help you.
CBOM tools FAQs
What is the difference between CBOM tools and SBOM tools?
SBOM tools inventory software components like libraries, packages and dependencies. CBOM tools focus specifically on cryptographic assets: algorithms, keys, certificates and protocols embedded across those components. CBOM extends the SBOM and adds the cryptographic layer that regulators now expect as a separate structured artefact.
Are CBOM tools mandatory under Indian regulations?
CERT-In’s Technical Guidelines Version 2.0 (July 2025) make CBOM mandatory for critical applications. RBI’s Advisory No. 11/2024 references these guidelines directly. Regulated entities should treat CBOM software as a compliance requirement rather than a best practice.
How do CBOM tools support post-quantum migration?
They build the cryptographic inventory that every NIST migration roadmap starts with. They identify quantum-vulnerable algorithms, prioritise applications by risk and track adoption of NIST-approved replacements. Without this inventory, PQC migration planning remains guesswork.
Can open-source CBOM tools meet enterprise compliance needs?
Some open-source options are well-suited to code-level scanning and CI/CD integration. For regulated enterprises requiring multi-source discovery, compliance-mapped reporting, on-premise deployment and continuous monitoring, a commercial platform is typically necessary.