Map cryptographic assets with
CBOM Solutions
Gain end-to-end visibility into your cryptographic posture, achieve compliance & prepare for post-quantum migration.
Talk to our Experts Today
INTRODUCTION
CyberNX CBOM Solutions
A Cryptographic Bill of Materials (CBOM) lists every cryptographic asset your firm depends on, like certificates, keys, algorithms and libraries. CyberNX makes CBOM generation and continuous monitoring effortless for regulatory readiness.

We address key challenges:
Crypto assets are scattered across code, cloud, HSMs & third-party libraries. We build a single, authoritative inventory per application.
RSA, ECC & Diffie-Hellman are quantum-vulnerable. We identify risky algorithms before migration pressure forces costly, rushed decisions.
RBI Advisory 11/2024 and CERT-In v2.0 mandate CBOM for regulated entities. We generate audit-ready compliance-ready CBOM from live data.
New vulnerabilities in cryptographic libraries go undetected for months. We monitor constantly and alert on changes that create real risk.
Managing CBOM across hundreds of apps manually is not possible. CyberNX automates generation, scoring and reporting at enterprise scale.
PROCESS
How It Works?
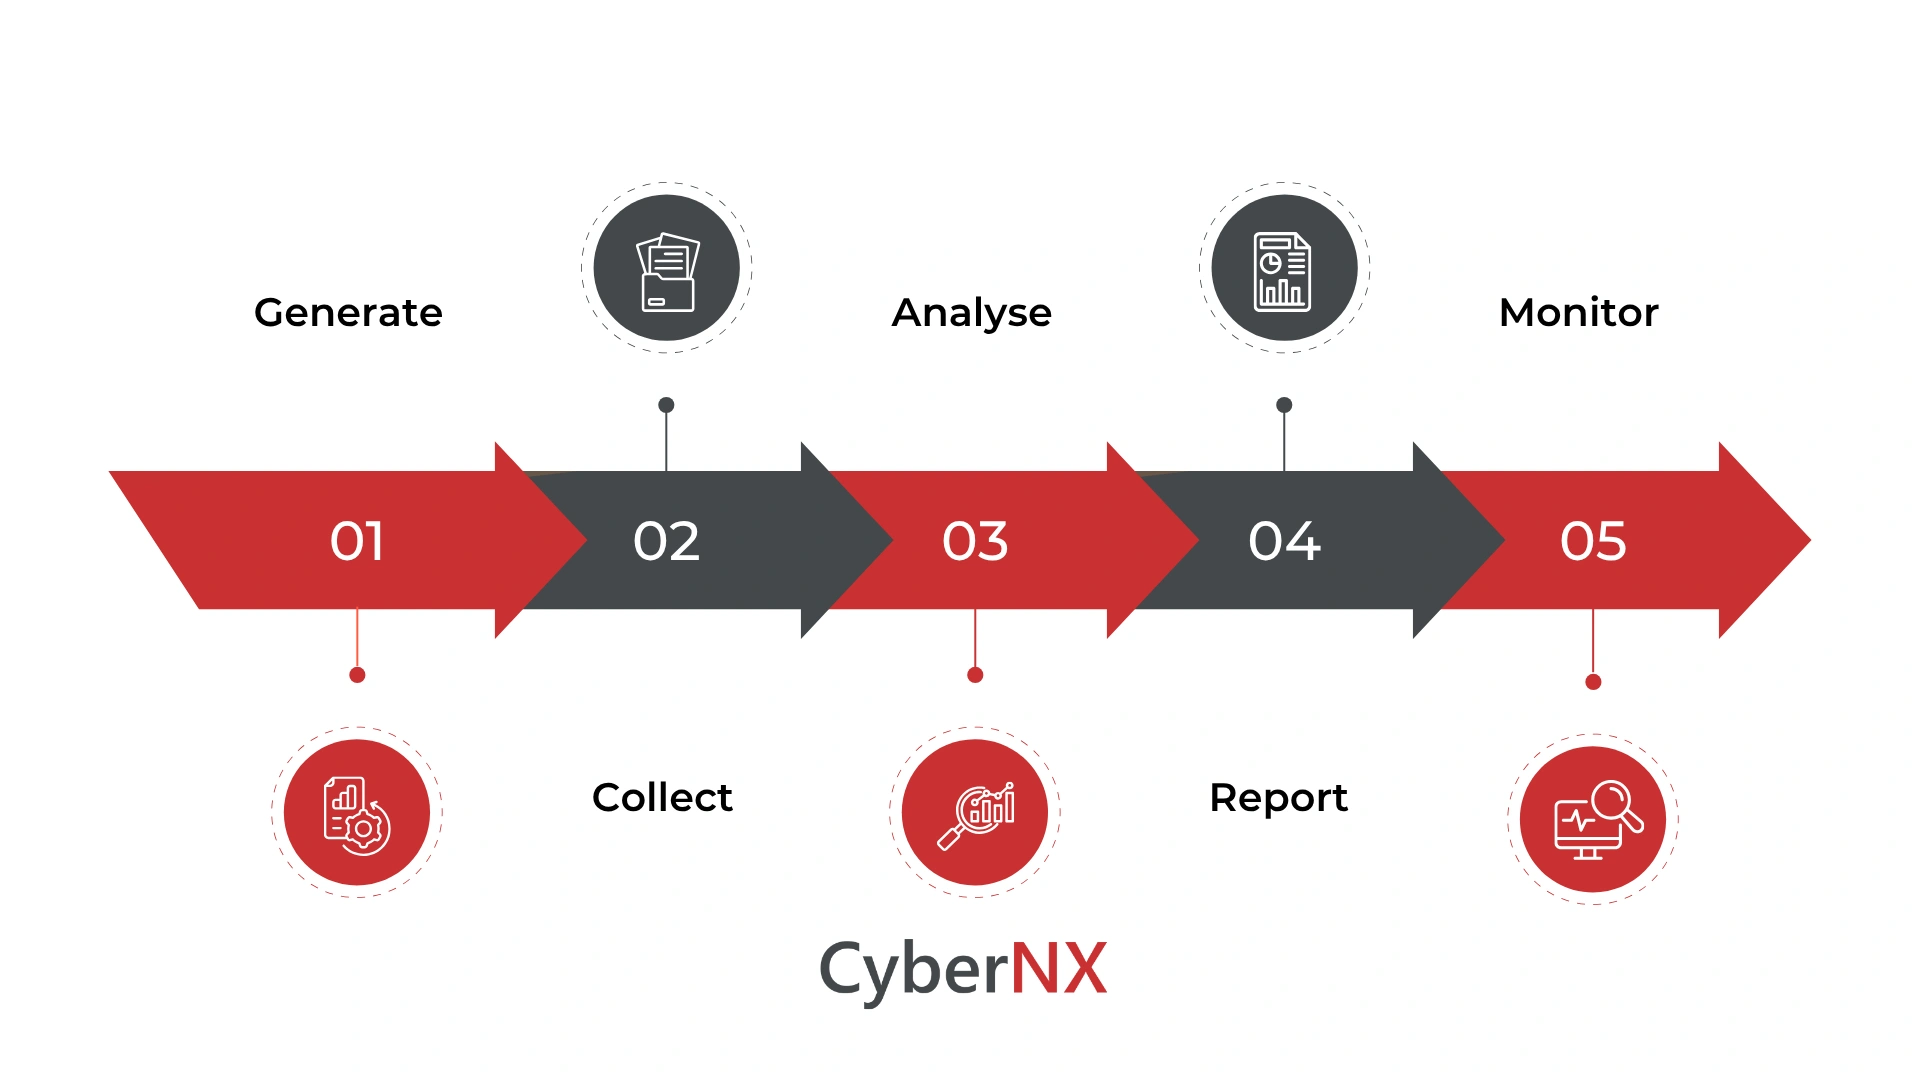
See every cryptographic asset across your systems with CyberNX CBOM Solutions
APPROACH
Why Choose CyberNX for CBOM Solutions?
CyberNX delivers CBOM as a complete managed capability. It is built by a team that runs penetration tests and red team exercises every day, which means findings are prioritised by exploitability, not just algorithmic classification.
Multi-Source Scanning
CyberNX combines network scans, code repository analysis, artifact scanning & HSM/KMS integration to build a complete CBOM per application.
Prioritised Reporting
Every finding is structured and prioritised in a thorough manner. Your teams get a clear action plan, not just a flat CSV of algorithm names.
Regulator-Ready Output
CyberNX maps findings directly to RBI Advisory 11/2024, CERT-In Technical Guidelines v2.0, NIST standards and the EU Cyber Resilience Act.
Post-Quantum Readiness
We detect quantum-vulnerable algorithms, tracks adoption of NIST-approved PQC algorithms and generates app-level migration roadmaps.
Flexible Deployment
We deploy as managed SaaS or on-premise in your VPC or data centre, with full data residency for BFSI, defence and regulated sectors.
Customer first Approach is our guiding principle.
BENEFITS
CBOM Solutions
Complete Visibility
Know exactly which cryptographic assets are in use across every application - no gaps, no blind spots.
Quantum Risk Reduction
Identify quantum-vulnerable algorithms and plan a structured PQC migration before attackers act first.
Audit Readiness
Meet RBI and CERT-In expectations with evidence packs built from live CBOM data. No last-minute preps.
Faster Incident Response
When a cryptographic vulnerability hits, NXRADAR finds every affected app instantly - in hours not weeks.
Crypto-Agility Built In
Replace vulnerable algorithms without guesswork. Our solution keeps the full cryptographic identity you need.
Scalable Management
Our solution manages CBOM generation and monitoring across hundreds of applications, without scaling your team.
For Customized Plans tailored to Your Needs,
Get in Touch Today!
FAQs
Frequently Asked Questions
A CBOM is a structured inventory of every cryptographic asset in your systems – certificates, keys, algorithms, protocols and libraries. It gives your firm complete visibility into its cryptographic posture.
RBI Advisory No. 11/2024 references CERT-In Technical Guidelines v2.0, which mandate CBOM for regulated entities and critical-infrastructure operators. Our solution generates the required inventory and audit evidence directly from live data.
Our solution includes advanced tool that scans across four sources – network, code repositories, build artifacts and HSM/KMS integrations – and merges the findings into a single deduplicated CBOM per application.
Our Solution identifies quantum-vulnerable algorithms across your systems, tracks adoption of NIST-approved PQC algorithms and generates per-application migration roadmaps with a PQC readiness score. It gives your team a clear baseline and action plan for the transition.
RESOURCES