Every developer will have a familiar complaint about their code scans. Static testing tools may find plenty of issues, but many turn out to be false alarms. Teams can waste hours separating genuine vulnerabilities. Meanwhile, developers are shipping code faster than ever, and AI assistants are writing much of it.
This is where AI SAST comes in. It aims to improve vulnerability detection, provide better context, and speed up fixes. But does it really deliver on these promises? And can it create new challenges for security teams?
Let’s understand what AI SAST is, how it improves static testing, and what to look for before choosing a tool.
What is AI SAST?
Before we get into the benefits, let us get the basics right.
Static Application Security Testing (SAST) reviews source code without executing it. It looks for vulnerabilities like injection points, weak encryption and unsafe data handling. Traditional tools do this through predefined checks and pattern matching. That works well for known issues but struggles with anything unusual.
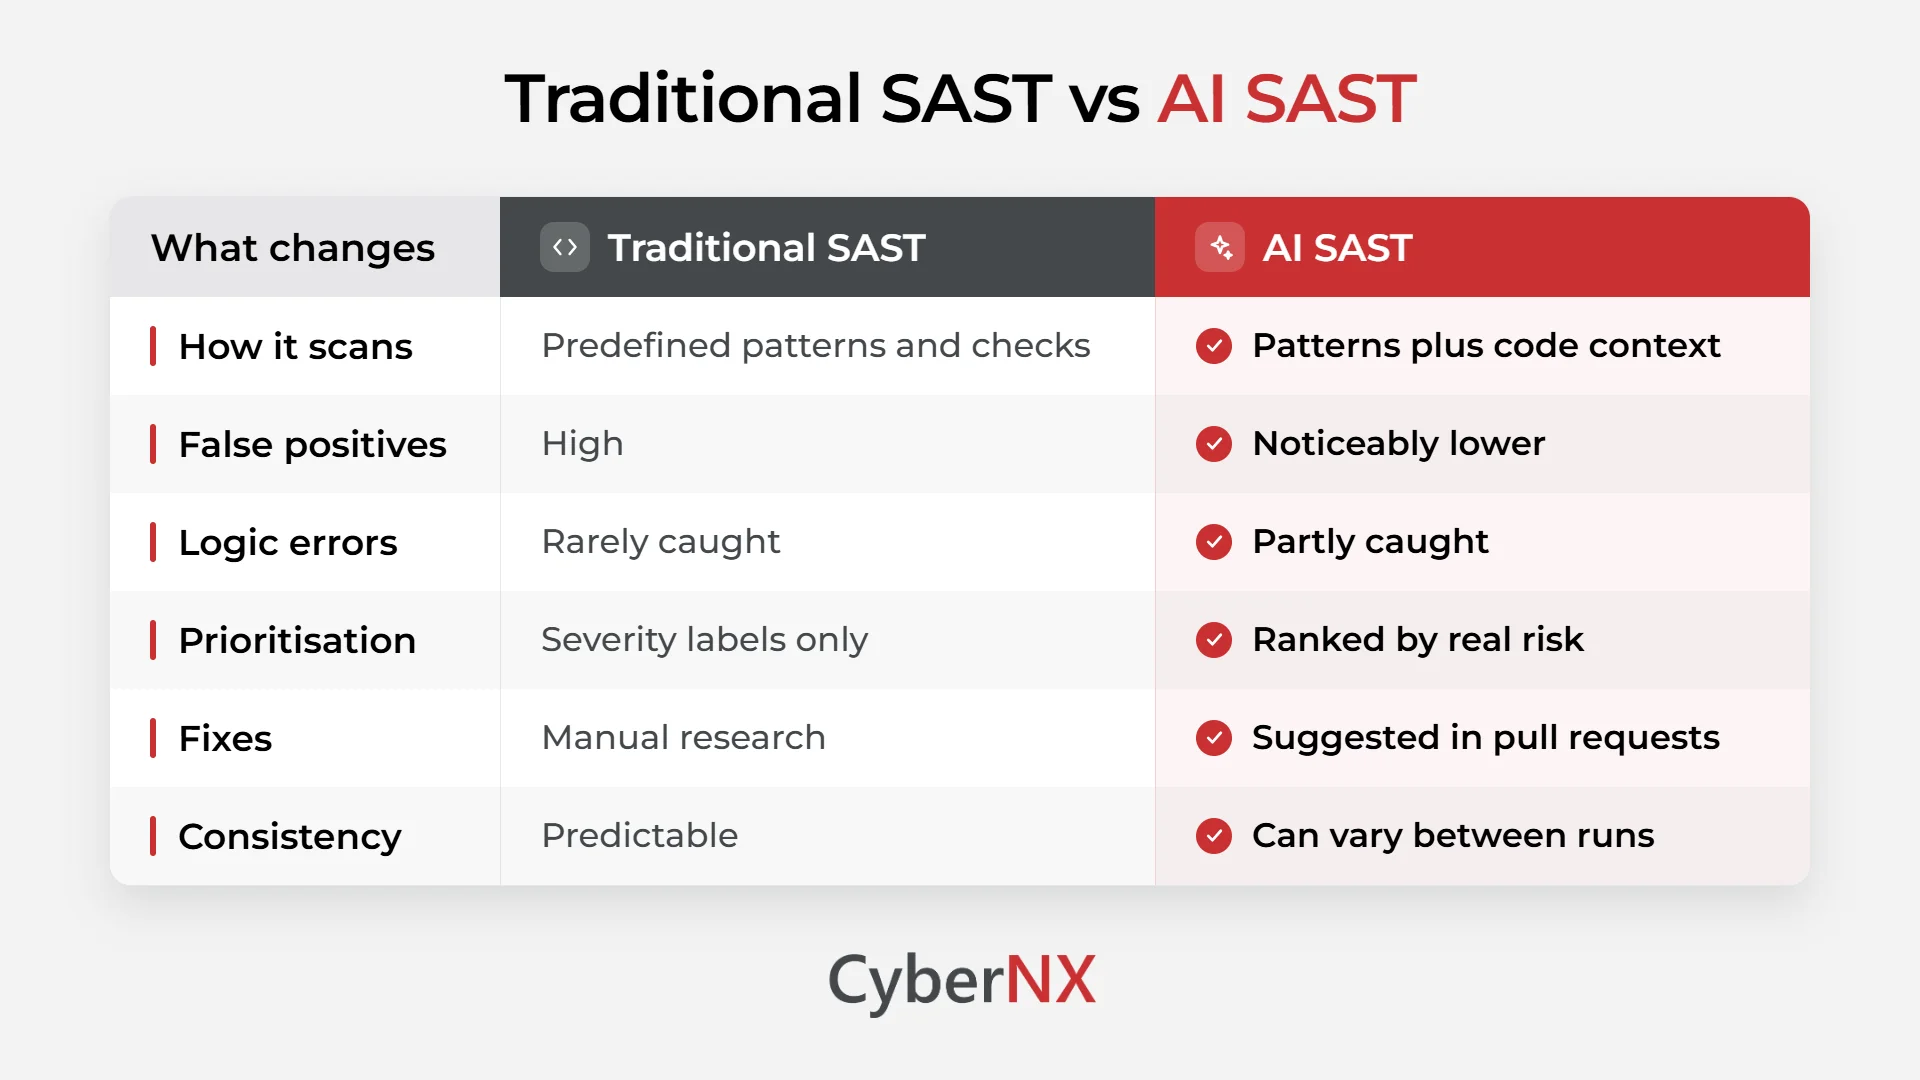
AI SAST adds machine learning and large language models to this process. Rather than just matching patterns, it tries to grasp what the code really does. It traces how data moves between functions, files and services. The result is a scan that reads code more like a human reviewer.
Pattern-based scanning vs AI-powered SAST
A pattern-based scanner works much like a spell checker. It flags any word it does not recognise, even correct ones. An AI-powered SAST tool behaves more like an experienced editor. It reads the full sentence and evaluates the meaning before raising a concern.
In practice, most modern tools blend both methods. Predefined checks still detect well-known patterns quickly and cheaply. The AI layer then adds context, ranks the findings and proposes fixes.
How AI SAST makes static testing more effective
The real gains show up in everyday work, where accuracy and speed matter most.
Far fewer false positives
False positives are the top complaint about legacy SAST. A scanner may flag a database query, even when the input is already sanitised. An AI model can follow that input and spot the validation step. As a result, irrelevant alerts drop and genuine issues stand out.
Smarter prioritisation
Not every vulnerability carries the same weight. AI SAST can weigh reachability, exposure and the sensitivity of the data involved. A vulnerability in a public payment API outranks one in a test script. Ranking findings this way helps your team tackle what truly matters first.
Detecting logic errors that pattern checks miss
Pattern-based checks struggle to spot issues without a known signature. Broken access checks and business logic errors are classic examples. Because AI models read intent, they can surface some of these gaps. They are not perfect here, but they detect more than predefined checks alone.
Quicker fixes inside the developer workflow
Many tools now suggest code fixes directly in pull requests or code editors. Developers see the issue, the reason and a possible patch in one place. This shrinks the time between detection and remediation. It also helps newer developers build secure coding habits along the way.
Keeping pace with AI-written code
Coding assistants now produce code at a speed manual review cannot match. That code often looks clean but can hide insecure defaults. AI SAST scans at the same pace, so security does not become the bottleneck.
The flip side: Where AI SAST can fall short
No scanner is flawless, and AI-based testing brings its own trade-offs.
Alert fatigue does not simply vanish
Here is the challenge many teams discover after rollout. AI reduces irrelevant alerts, but it does not remove them. Some tools widen coverage, which can mean more findings overall. When everything is labelled critical, nothing feels urgent any more. Over time, people start ignoring alerts, and real vulnerabilities slip through.
Inconsistent or invented findings
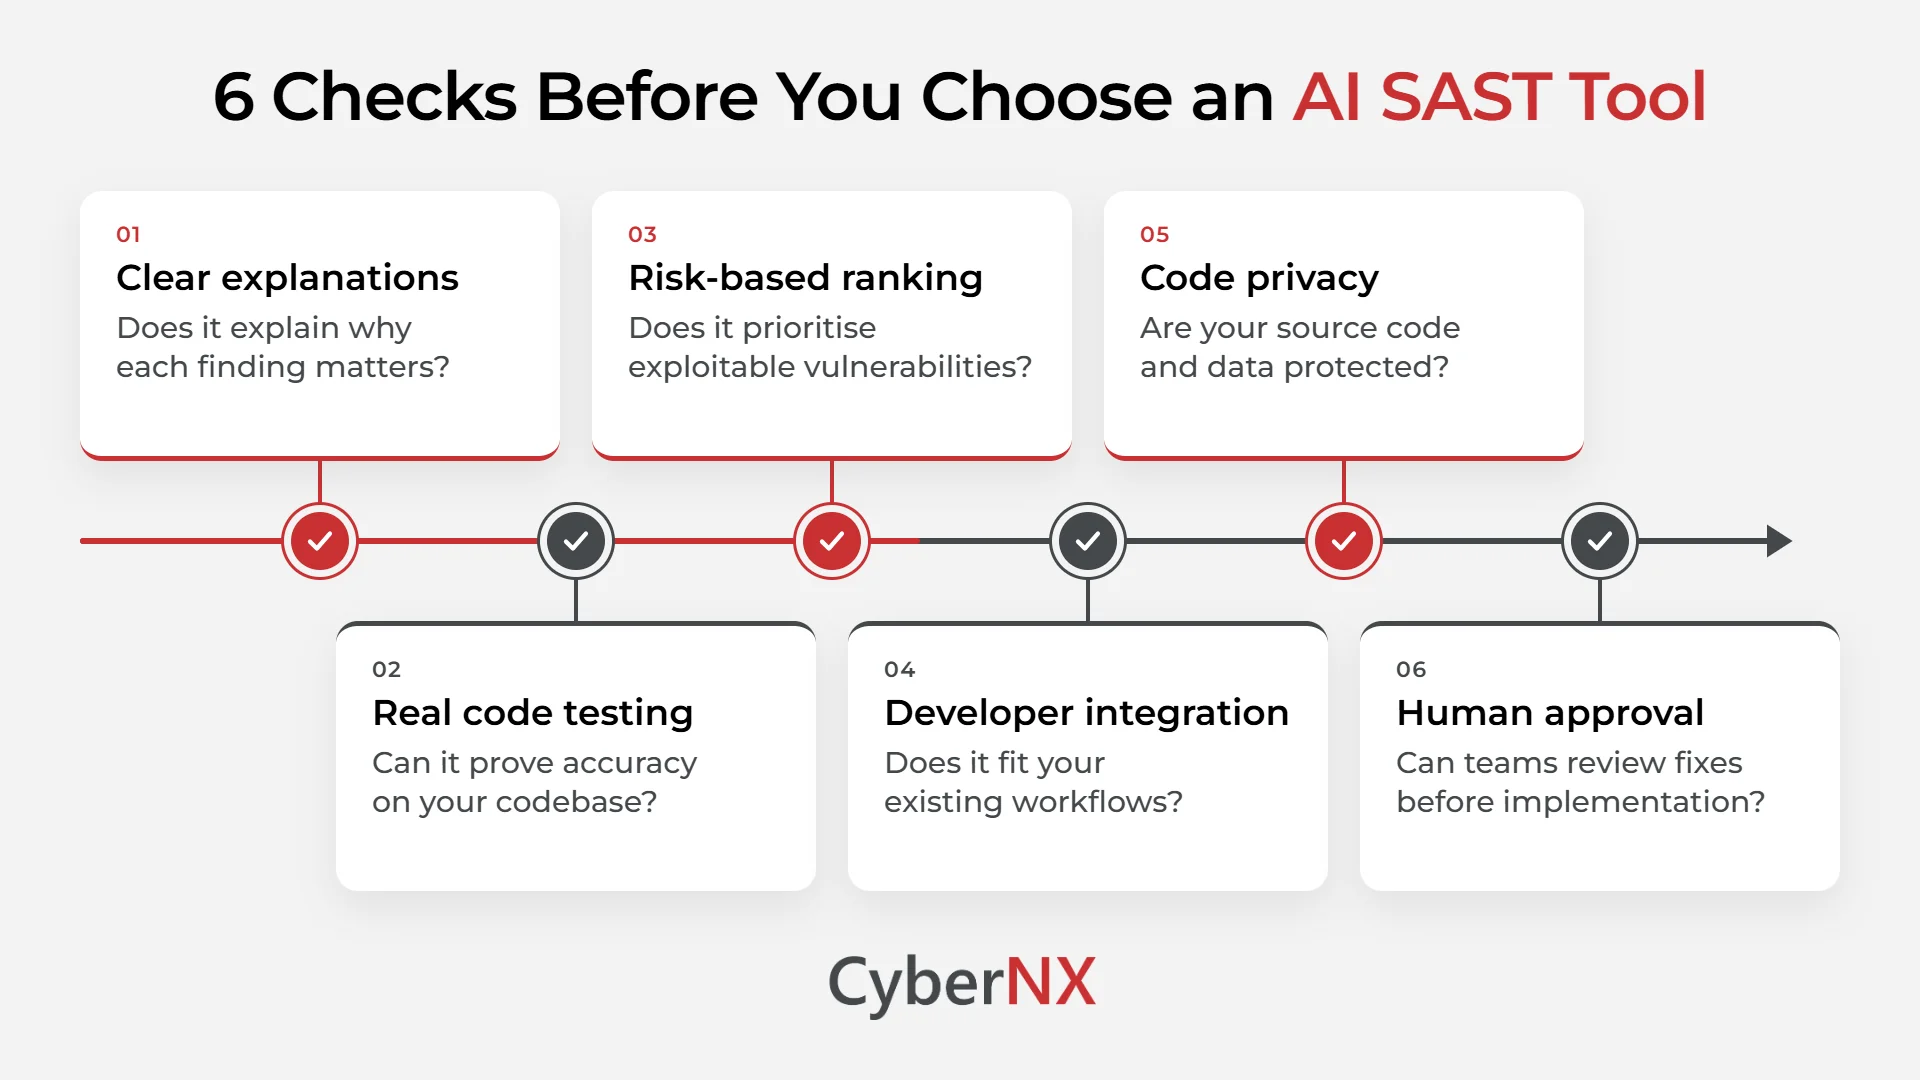
Language models work on probability, not strict logic. The same code can return slightly different results on separate runs. Models can also report issues that do not exist. In some cases, a suggested fix may resolve one issue and break another. Every AI-generated patch still needs a human review.
Limited explainability
Some tools flag a problem without showing the reasoning behind it. Without a clear data flow, developers struggle to trust or verify the alert. Auditors may also question findings that lack traceable evidence.
Data privacy and cost concerns
Cloud-based scanning may send your source code to third-party servers. For regulated sectors like banking, that raises serious data residency questions. Scanning large codebases with heavy models can also increase costs quickly.
What to look for in an AI SAST tool
The right tool should reduce your team’s workload, not add to it. But before finalising solutions, it is important to understand what you should look for in an AI SAST tool.
Finally, remember that AI SAST is one layer, not a complete programme. Pair it with dependency scanning, dynamic testing and manual penetration testing. Each method detects what the others tend to miss.
Conclusion
Here is what it all comes down to for your security programme.
AI SAST is a genuine step forward for static testing. It reduces false positives, ranks risk better and helps developers fix vulnerabilities faster. Yet it is not a complete answer on its own. Without tuning and oversight, it can overwhelm your team with new alerts.
The strongest approach pairs good tooling with expert validation. That is where we come in. At CyberNX, our secure code review service combines automated scanning with manual expert analysis.
Our specialists validate what your scanners report and confirm the risks that matter. We discard false alarms and uncover the vulnerabilities automated tools miss. You also get clear, prioritised guidance your developers can act on quickly. Ready to find out how secure your code really is? Talk to our team today.
AI SAST FAQs
Here are answers to questions we often hear from security teams.
Does AI-powered SAST replace manual code review?
No, it supports it rather than replacing it. The tool handles volume and filters out obvious false positives. Human reviewers still assess complex logic, design weaknesses and suggested fixes.
Can it scan code written by AI coding assistants?
Yes. It scans any source code, whoever or whatever wrote it. AI-written code benefits most, since it can hide insecure defaults that look harmless.
How is AI SAST different from dynamic testing?
Static testing checks source code before the application runs. Dynamic testing probes a running application from the outside, much like an attacker. Both are useful, and they work best together.
Is it safe to share source code with an AI scanning tool?
That depends on the vendor’s data handling. Check where code is processed, how long it stays and whether it trains models. Private or on-premises deployment suits sensitive codebases best.
How can we reduce alert fatigue after adopting AI SAST?
Set clear severity thresholds and route findings straight to code owners. Suppress known safe patterns and revisit tuning every few months. A trusted partner can also handle triage, so your team sees only validated issues.