Software Bill of Materials (SBOMs) are critical for security and crucial for compliance. In a world where software combinations exponentially increase every day, you need clear, dependable inventory. And although SBOM is the inventory, but SBOM standards and formats like CycloneDX and SPDX are the building codes that make that inventory trustworthy, machine-readable and actionable. Therefore, understanding its nuances, complexities and benefits are important to explore its potential, and to meet regulatory mandates.

In case you want to do a deep dive into SBOM and understand every facet of it, Download our Whitepaper Software Bill of Materials (SBOM): Building Software Transparency and Regulatory Confidence for Indian Enterprises
What are SBOM Standards and Why it is Important?
SBOM standards essentially establishes the way to structure software composition data and offers SBOM format for everyone. How it helps is that everyone can express what’s inside the software using it.
It defines the required fields of an SBOM (component identifiers, versions, supplier, hashes and dependency relationships). Plus, it shows how those fields are expressed.
One obvious question is how such standards came into existence? National Telecommunications and Information Administration (NTIA) and similar organizations came together to shape such a framework.
Also, SBOM standards enable automated consumption. For instance, an SBOM produced by one tool can be read, analysed and correlated with vulnerability feeds by another. Without shared standards, organisations spend time translating bespoke SBOMs rather than acting on them.
SBOM standards remove that ambiguity and free security teams to automate detection and remediation.
SBOM Formats: A Deep Dive
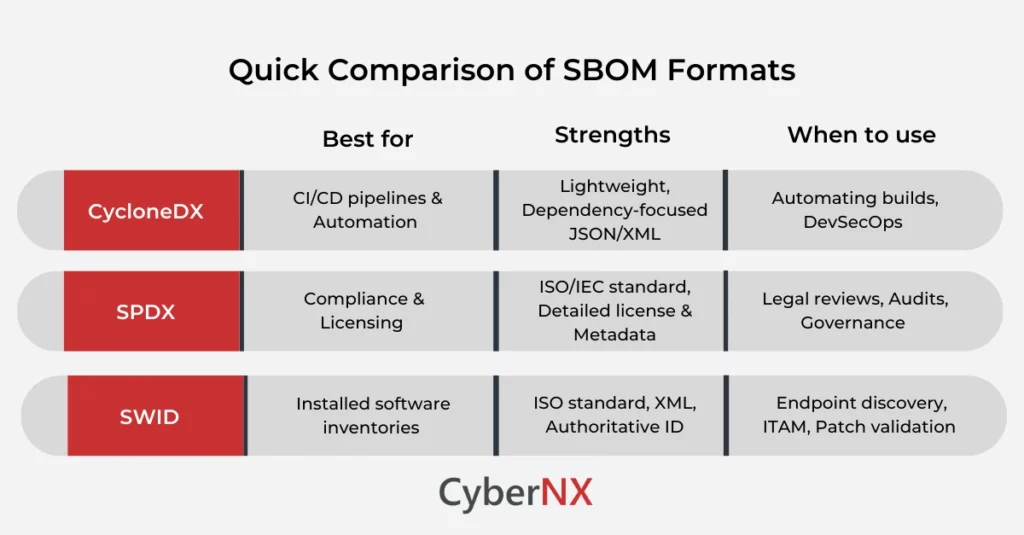
Three formats are integral to modern SBOM programs: CycloneDX, SPDX and SWID. Each was designed with a slightly different use-case and toolchain in mind, so choosing or supporting all three gives you the freedom to meet engineering, security and regulatory needs without translation bottlenecks.
1. CycloneDX
CycloneDX was built for rapid automation in CI/CD pipelines and for security workflows that need compact, machine-friendly BOMs. It has JSON and XML serializations and a focused schema for components. Plus, it has dependencies and explicit fields for vulnerability and component metadata that security tools expect.
CycloneDX is intentionally pragmatic: minimal required fields, strong support for transitive dependency graphs and rich extension points (vEX/VEX, hashes, purl identifiers). These features make it easy to integrate with scanners, registries and pipeline automation. These traits make CycloneDX ideal when your goal is automated scanning, lightweight storage of BOMs in artifact repositories and fast programmatic queries.
Practical notes:
- Typical files: bom.json (CycloneDX JSON) or XML equivalent; spec includes a JSON schema for validation.
- Strengths: compact, CI/CD-friendly, excellent tooling for vulnerability matching and conversion to VEX.
- When to pick it: embed SBOM generation into pipelines, perform automated vulnerability triage and operate a BOM repository for DevSecOps teams.
Current version note: CycloneDX 1.7, released October 2025, is the active specification. Many CI/CD tools still generate 1.5 or 1.6 output by default. Before treating a tool’s SBOM as compliant, confirm the specVersion field in the output. CERT-In and SEBI do not mandate a specific version number, but auditors increasingly check whether the file validates against a current schema. CycloneDX has also extended beyond software SBOMs to cover CBOM (cryptographic), HBOM (hardware), and ML-BOM (machine learning) within the same specification family – relevant for regulated entities now navigating CERT-In v2.0’s expanded BOM taxonomy.
2. SPDX
SPDX is the heavyweight, standards-backed format focused on legal provenance, license declarations and rich metadata about packages and their relationships.
It is an internationally recognised open standard (ISO/IEC-backed) with a detailed model for license identifiers, copyright statements and granular provenance (who produced what, when, and under which license).
SPDX has multiple serializations (tag/value, RDF, JSON) and a mature ecosystem of converters and compliance tools. If your SBOM objective includes auditability for IP/licensing reviews and cross-project compliance, SPDX is frequently the best fit.
Practical notes:
- Typical files: .spdx.json, .spdx (tag/value) or RDF serializations for integration with semantic tooling.
- Strengths: rich licensing vocabulary (SPDX License List), provable provenance, strong adoption in open-source and enterprise compliance workflows.
- When to pick it: legal/compliance-heavy programs, supplier audits, projects where license clarity and provenance are governance priorities.
Current version note: SPDX 3.0 (published 2024) introduced a significant structural change – it moved from a package-and-relationship model to an element-based, linked-data model. Elements (packages, files, snippets, AI datasets) are connected through typed relationships and can reference external documents. This is more powerful for complex, multi-team supply chains but adds modelling complexity. Many tools still produce SPDX 2.3 output; check your tool’s default and whether your regulator’s validation tooling accepts 3.0 before upgrading. For most BFSI compliance purposes, SPDX 2.3 remains fully valid.
3. SWID (ISO/IEC 19770-2) – A Note on Current Relevance
SWID tags were historically listed alongside CycloneDX and SPDX as one of three SBOM formats, primarily because the 2021 NTIA minimum elements recognised all three. That changed with the 2026 CISA Minimum Elements guidance, which dropped SWID entirely, leaving CycloneDX and SPDX as the two accepted formats.
This reflects a broader practitioner consensus: SWID is not an SBOM format in the same sense. Where CycloneDX and SPDX describe what went into building software – its dependencies, libraries, and transitive components – SWID identifies what is installed on a specific endpoint device. It answers a different question and serves IT Asset Management rather than software supply chain security.
SWID retains relevance in two narrow contexts: US federal government endpoint inventory programs where NIST guidance still references it, and as embedded metadata within CycloneDX components (the CycloneDX spec includes a SWID field for commercial software identification). For most security and compliance teams – and for all Indian regulated entities under RBI, SEBI, and CERT-In SWID does not feature in any regulatory expectation. Your compliance work begins and ends with CycloneDX and SPDX.
Interoperability, Conversion and Real-World Choices
In practice, organisations don’t pick a single format and stop there – they use a combination:
- CycloneDX for build-time automation and vulnerability workflows.
- SPDX for compliance and provenance reporting.
Most modern toolchains can emit CycloneDX or SPDX and include converters (or libraries) to translate between them. Conversion helps meet partners’ and regulators’ requirements without changing your internal pipelines. That said, conversion is not always lossless: SPDX’s deep licensing/provenance fields may not map perfectly to CycloneDX’s installed-instance focus does not correspond one-to-one with build-time component graphs. Treat conversions as pragmatic bridges but retain canonical SBOMs in the format that best serves your primary workflow.
VEX and CSAF: What Makes SBOM Standards Operationally Useful
Vulnerability Exploitability eXchange – VEX
A format comparison answers what an SBOM contains. However, it does not answer if any new CVE comes up or component affects specific deployment. That answer comes from VEX, which is short for Vulnerability Exploitability eXchange.
A VEX document accompanies an SBOM and states, for each known vulnerability in a component, whether it is exploitable in this product’s context: affected, not affected (with a machine-readable justification), under investigation, or fixed. Without VEX, a security team receives a list of components and a list of CVEs and must manually determine which vulnerabilities require action. With VEX, that triage is documented, structured and auditable.
CSAF Common Security Advisory Format
It is the complementary standard for vendor-side vulnerability advisories. Where VEX is the producer’s statement about their product, CSAF is the supplier’s structured advisory about their component. When both are present, a security team can match an SBOM component to its vendor’s CSAF advisory and then to the product’s VEX assertion in a fully automated workflow.
CERT-In’s guidelines reference this chain explicitly: SBOMs should integrate with VEX and CSAF advisories for rapid vulnerability status updates, not just raw CVE lists. The 2026 CISA Minimum Elements guidance, released July 2026, went further – it added VEX linkage as a named minimum element, the first time exploitability context has been included at the baseline level.
Format implications: CycloneDX has native VEX support built into the specification. SPDX 3.0 introduced a vulnerability profile but VEX integration requires additional tooling in most pipelines. If your primary SBOM objective is vulnerability operationalisation, this is a practical reason to favour CycloneDX for your security workflow, even if you also produce SPDX for compliance reporting.
What SEBI, RBI and CERT-In Require from Your SBOM Formats
India’s three financial regulators – CERT-In, SEBI, and RBI – each define specific SBOM fields they audit, not just formats they accept. Choosing CycloneDX or SPDX is the first step; confirming your chosen format covers those fields without gaps is where most teams stumble. The format you pick determines how much manual enrichment your team carries to reach compliance.
For the complete field-by-field mapping of CERT-In’s 21 fields and SEBI’s 9 fields against CycloneDX and SPDX – including which fields are auto-generated, which are semi-automated, and which require manual input, read our detailed guide: Aligning SBOM Formats & Field Mapping with SEBI, RBI & CERT-In.
Read Related Blogs:
Understanding SBOM Requirement of SEBI CSCRF
CERT-In’s SBOM Guidelines Explained
How to Meet RBI SBOM Compliance
Bringing SBOM Standards into Your Organisation
Operational adoption is straightforward to describe and hard to execute without discipline. Start by embedding SBOM generation in CI/CD so every build produces a signed SBOM artifact. Validate SBOMs automatically, store them in a central repository and link entries to your vulnerability and vendor-risk systems.
Make SBOM delivery and timely updates contractual obligations for critical vendors so your procurement and security functions are aligned. Over time, this turns a compliance artifact into an operational control.
Common Pitfalls and How to Avoid Them
SBOM programs fail when inventories are partial, stale or unsigned. Common failures include missing transitive dependencies, inconsistent formats across teams and a lack of linkage to advisory or exploitability data. Avoid these by treating SBOMs as live artefacts. Generate them in CI, validate and sign them, normalise formats in a central store. Ensure they feed your vulnerability and vendor governance processes.
Practical tool support and clear owner responsibilities make SBOM programs sustainable and auditable over time. Sign SBOMs to protect integrity, and link SBOM entries to VEX/CSAF advisories so you can quickly assess exploitability and required actions.
Conclusion
SBOM standards and SBOM formats are the scaffolding that convert opaque component lists into repeatable, machine-actionable security capability. For CISOs, CTOs and founders: adopt pragmatic formats, automate SBOM generation and validation, and align processes to regulator expectations so transparency becomes resilience. SEBI and CERT-In have already provided operational guidance – use these signals to make SBOMs a living part of your security and procurement lifecycle.
Start today and make software transparency a competitive advantage. CyberNX’s SBOM solutions generate and manage SBOMs in CycloneDX, SPDX, and other formats continuously and not once a quarter with pre-mapped fields for CERT-In, SEBI, and RBI built in. Talk to our experts to see how it fits your compliance program.
SBOM Standards FAQs
What problem do SBOM Standards solve for business leaders?
SBOM Standards remove ambiguity by ensuring every software inventory follows a consistent, machine-readable structure. This makes it easier for CISOs and executives to track risks, meet regulatory expectations, and respond faster to vulnerabilities.
How do CycloneDX, SPDX, and SWID differ in real-world use?
CycloneDX is designed for CI/CD automation, SPDX is rich in licensing and provenance data for compliance, and SWID identifies installed software on devices. Many organisations adopt a hybrid approach to cover all use cases.
Why are regulators like SEBI, RBI, and CERT-In emphasizing SBOM Standards?
These regulators see SBOMs as a way to improve cyber resilience across financial and critical sectors. By mandating or recommending SBOM practices, they ensure organisations can prove software transparency and respond effectively to supply-chain threats.
How should enterprises start implementing SBOM Standards?
Begin implementing SBOM standards with small pilots in CI/CD pipelines to generate CycloneDX SBOMs, add SPDX for compliance artefacts, and integrate SWID into endpoint management. Over time, link SBOM data to vulnerability feeds and vendor risk management for full coverage.