Achieve security, visibility & compliance
SBOM Solutions
End-to-end SBOM solutions to secure software supply chains, ensure component visibility and maintain compliance.
Talk to our Experts Today
INTRODUCTION
Better Security & Compliance with CyberNX SBOM Solutions
Enhance your security and compliance posture with CyberNX’s SBOM solutions, delivering deep component insights, automated vulnerability detection and compliance tracking and reporting aligned to SEBI, RBI and CERT-In.
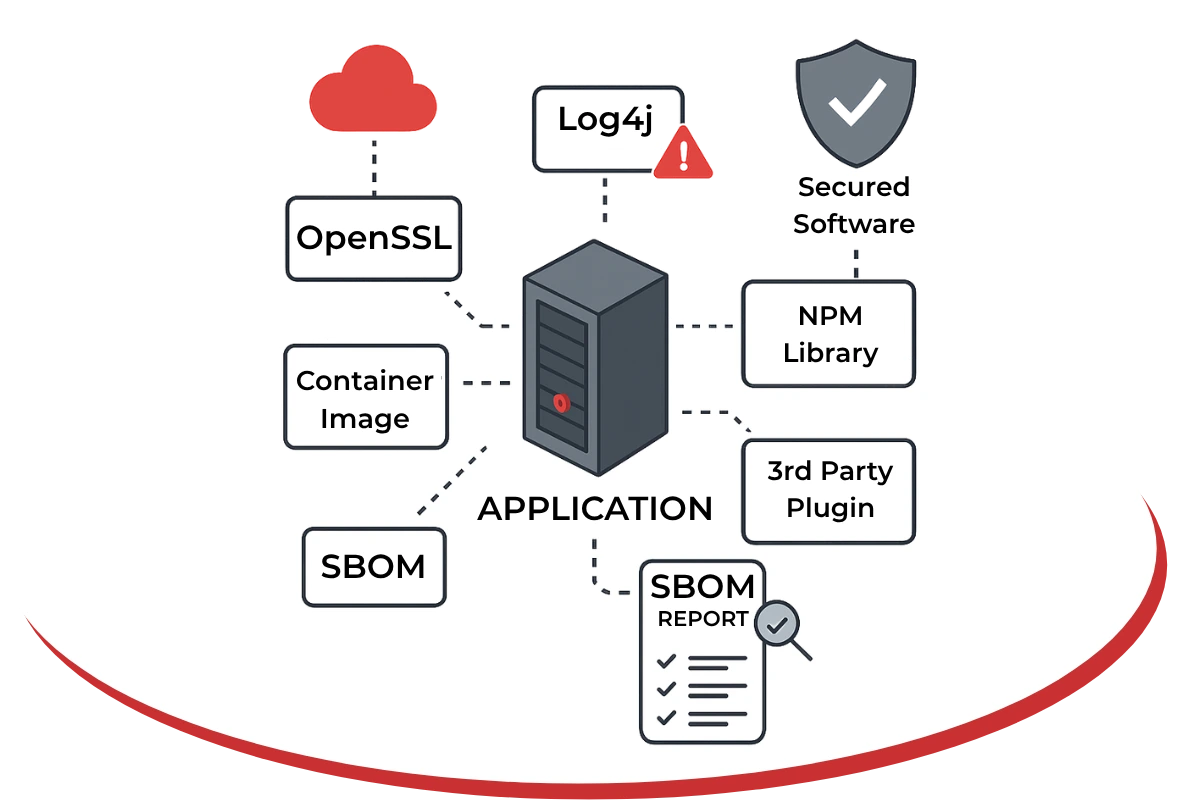
Key Features:
Live inventory across source code, binaries, containers & vendor software, covering direct and transitive dependencies.
Components matched against NVD, OSV, GitHub Advisory and vendor feeds. Checks new CVEs surface affected applications.
Licences classified across permissive, copyleft & proprietary types. Incompatible or licences flagged before exposure.
Third-party SBOMs are accepted, validated and enriched. Plus, SBOM governance is extended to your entire supply chain.
We support CycloneDX and SPDX across SaaS, private cloud and on-premise. Completely portable with no residency trade-offs.
Identify cryptographic assets linked to software components, detect algorithms, track certificates & flag PQC readiness.
PROCESS
How It Works?
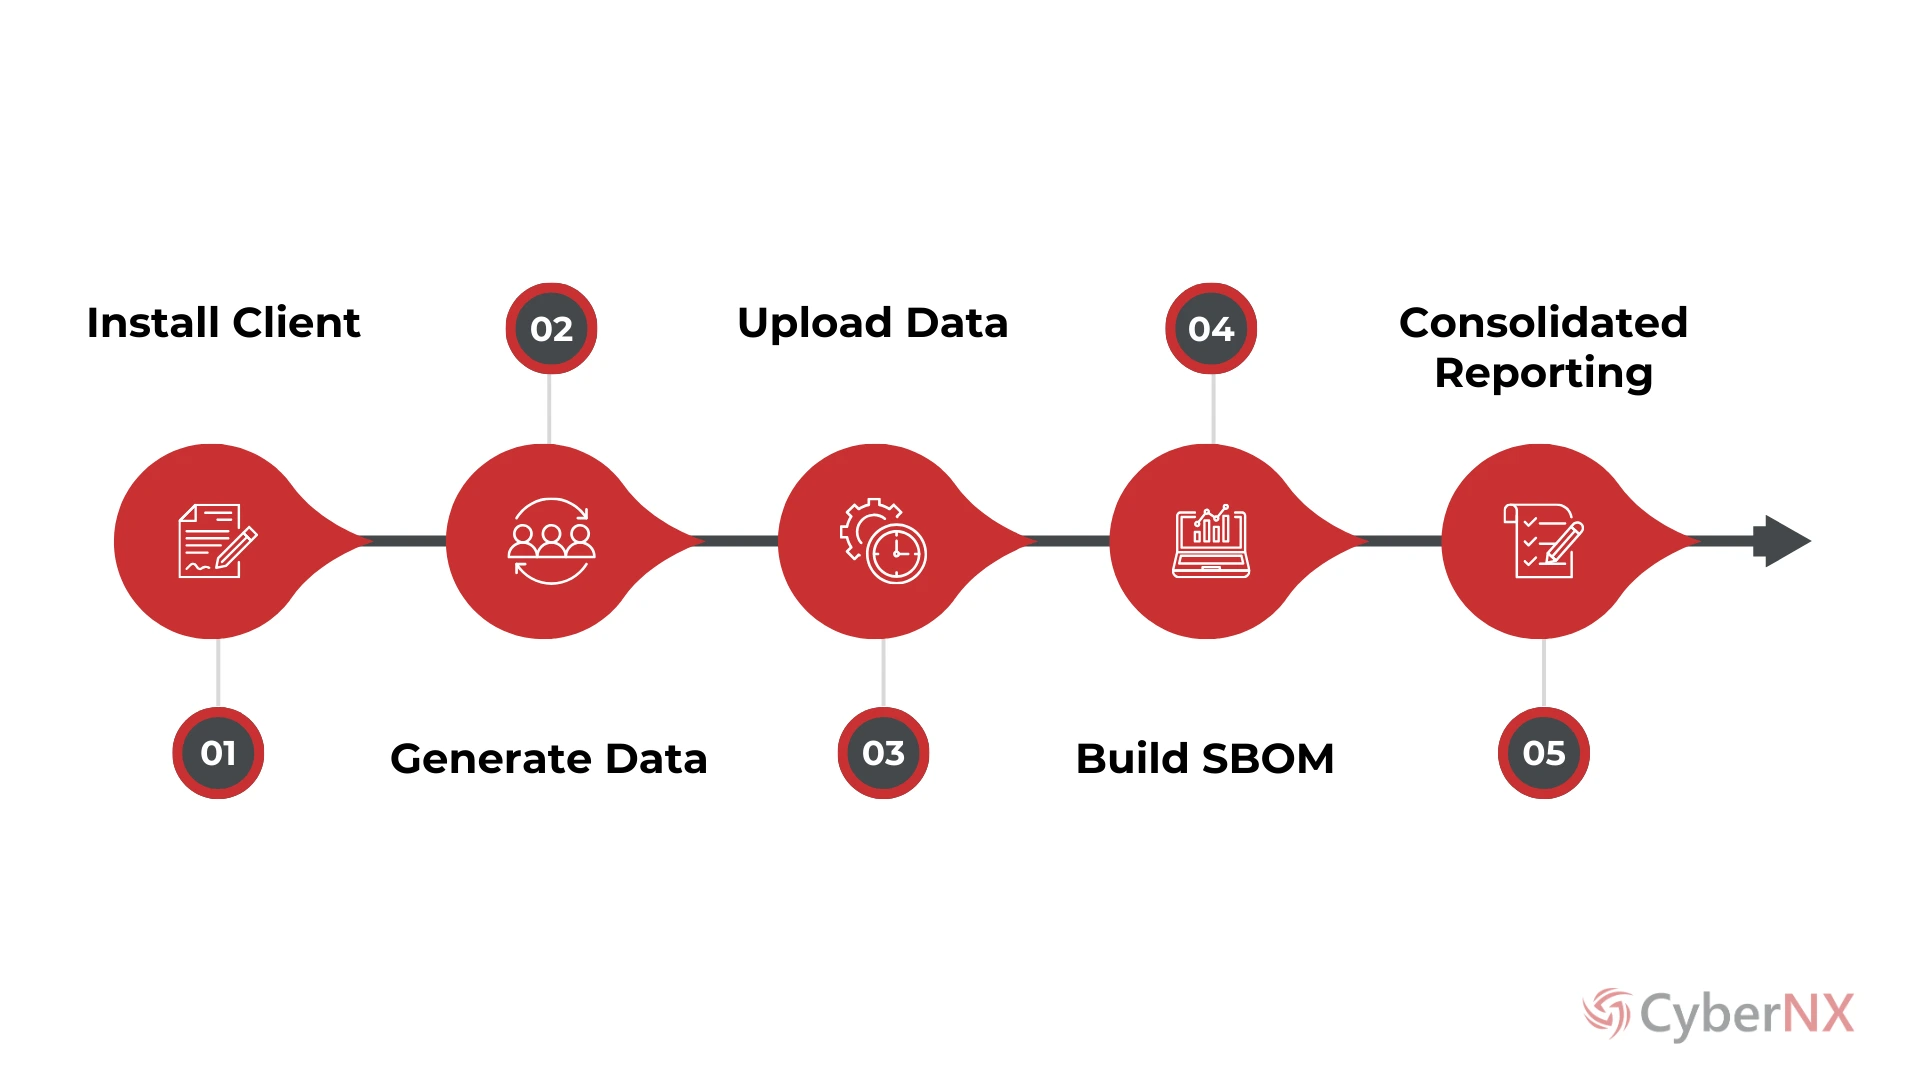
Secure Your Software Supply Chain with Our SBOM Solutions
APPROACH
Why Regulated Enterprises Choose CyberNX SBOM Solutions?
CyberNX delivers a governed SBOM capability powered by an advanced in-house SBOM tool and offers regulatory expertise and managed delivery for regulated enterprises and those seeking software security.
AI enrichment
Missing metadata inferred automatically – component origin, supplier and licence filled in, with unknowns flagged for human review.
Regulatory precision
SBOMs pre-mapped to CERT-In 21 fields, SEBI 9 fields and RBI as mandated plus audit outputs ready without need for manual mapping.
Enterprise governance
Role-based access, tamper-proof audit logs and immutable versioning which enables chain of custody for regulators and auditors.
Smart prioritisation
Vulnerabilities ranked by CVSS, EPSS, reachability & business criticality to remediate what is genuinely exploitable.
Continuous coverage
SBOMs auto-regenerate on every build, tracking component changes across environments and it is never filed as a one-off.
Flexible deployment
SaaS, private cloud or on-premise – identical capabilities, no trade-offs for entities with data residency requirements.
Customer first Approach is our guiding principle.
BENEFITS
Our SBOM Solutions: Automated, Scalable and Compliant
Enhanced security
A zero-day lands and your cybersecurity team identify every exposed application before the window closes in minutes and not days.
Risk management
Remediation effort goes where it matters - backed by real exploitability and business criticality data, not CVSS rankings alone.
Regulatory compliance
Audit evidence generated continuously and available on demand - no last-minute scramble, no penalty exposure from compliance gaps.
Complete transparency
Licence obligations visible before they create legal risk. Vendor exposures known before they become your problem to fix.
Tailored deployment
On-premise, private cloud or SaaS - your data stays within your boundaries and your compliance posture stays intact.
Future readiness
Cryptographic governance & post-quantum readiness built in the same platform that covers SBOM today covers CBOM tomorrow.
For Customized Plans tailored to Your Needs,
Get in Touch Today!
FAQs
Frequently Asked Questions
An SBOM solution covers generation, management and governance – component discovery, vulnerability linkage, licence tracking and compliance reporting across your portfolio.
SEBI CSCRF mandates SBOM for regulated entities. CERT-In defines required fields and formats. RBI expects SBOM-driven risk programmes. CyberNX maps to all three.
Generation creates the inventory. Management keeps it current, links to vulnerability feeds, tracks licence obligations and produces audit-ready evidence on demand. CyberNX delivers both.
One-time generation typically takes 2-3 weeks. Quarterly setup with first-time scanning can be completed in 3-4 weeks.
Our in-house SBOM tool supports CycloneDX and SPDX – formats recommended by CERT-In for machine-readable exchange and other regulatory-accepted formats.
Yes. We support Docker containers, Kubernetes deployments and traditional server-based applications. Our agents scan container images and running containers.
No personal or sensitive data is captured. The SBOM contains only components, licences, dependencies and metadata required for function.
No. Lightweight agents run with minimal system impact without requiring application downtime. Scanning runs in the background without affecting performance.
RESOURCES