Attackers no longer just target your passwords; they are now searching for vulnerabilities in your software or applications. And the 2026 Verizon Data Breach Investigations Report proves it. It found that attackers used software vulnerabilities to get initial access in 31% of breaches. For the first time in cybersecurity history, this has become the most common way attackers break in.
That shift has made SAST vs DAST vs SCA a regular debate in security reviews. Many teams pick one tool and assume their applications are fully covered. In practice, each test sees a different layer of risk.
Below, we break down what each test covers and where it fits in your pipeline. We also show where all three still need human expertise.
Where risk actually hides in your applications
Before comparing tools, it helps to map where risk enters an application. In our experience, it comes from three distinct places.
1. The code your team writes
Your developers build business logic, APIs and authentication flows every sprint. One unsanitised input or hardcoded secret here can expose sensitive customer data. Since this code is proprietary, no public database will warn you about it. Only testing designed for custom code can surface these issues early.
2. The open-source code you depend on
Modern applications borrow heavily from open-source libraries and frameworks. Black Duck tracks this in its 2026 Open-Source Security and Risk Analysis (OSSRA) report. It found open source in 98% of audited codebases. Each package also pulls in transitive dependencies your team may never review.
3. How your application behaves once deployed
Some weaknesses only appear when the application runs in a real environment. Misconfigured servers, exposed admin endpoints and weak TLS settings are common examples. None of these become visible by reading source code alone. A strong testing programme needs to cover all three areas, not just one.
SAST vs DAST vs SCA: What each test actually does
Each tool maps neatly to one of those three risk areas. Here is how they work and what they bring to your security programme. Think of them as layers that cover each other’s blind spots.
SAST reviews your code before it runs
Static Application Security Testing (SAST) analyses source code, bytecode or binaries without executing them. It traces how untrusted input travels through your code towards sensitive functions. This is white-box testing, because the tool sees everything inside the application.
SAST is especially useful for detecting:
- Injection risks such as SQL injection and cross-site scripting (XSS) in custom code
- Hardcoded credentials including API keys, tokens and database passwords
- Insecure cryptography such as outdated algorithms or poor key handling
The trade-off is false positives. SAST cannot see runtime context, so some findings need manual validation.

Explore how AI SAST is improving code analysis and helping teams detect security issues in AI-generated code.
DAST tests your running application from outside
Dynamic Application Security Testing (DAST) interacts with a live application like an external attacker would. It sends crafted requests and studies the responses for signs of weakness. No source code access is needed, which makes this black-box testing.
DAST is valuable for commercial off-the-shelf (COTS) software you cannot inspect internally. It uncovers broken authentication, server misconfigurations and insecure session handling. Modern DAST tools also test REST and GraphQL APIs, not just web pages. However, DAST cannot point you to the exact line of code behind an issue.
SCA tracks the components you did not write
Software Composition Analysis (SCA) inventories every open source and third-party component in your application. It then matches those components against known vulnerability databases. Most SCA tools also flag licence conflicts and outdated packages.
The scale here is significant. The same OSSRA report found 87% of codebases had at least one open source vulnerability. Mature SCA tools prioritise findings by whether the vulnerable function is actually reachable. Still, SCA does not analyse the logic your own developers write.
SAST vs DAST vs SCA comparison
This side-by-side view shows how the three tests differ across the factors that matter most.
| Factor | SAST | DAST | SCA |
| What it scans | Proprietary source code | Running application | Open source and third-party components |
| Testing approach | White-box | Black-box | Component inventory and matching |
| Source code needed | Yes | No | Manifest or build files |
| Best SDLC stage | Coding and commit | Staging and pre-production | Build and post-release |
| Typical findings | Injection risks, hardcoded secrets | Misconfigurations, authentication gaps | Known Common Vulnerabilities and Exposures (CVEs), licence conflicts |
| Main blind spot | Runtime behaviour | Root cause in code | Custom application logic |
| Feedback speed | Fast, close to the developer | Slower, late in the cycle | Fast, at every build |
Notice that no single column covers every risk on its own. SAST and SCA work early and fast, while DAST confirms what is truly exploitable. Together, they give your teams visibility from the first commit to production.
How to place each test in your SDLC
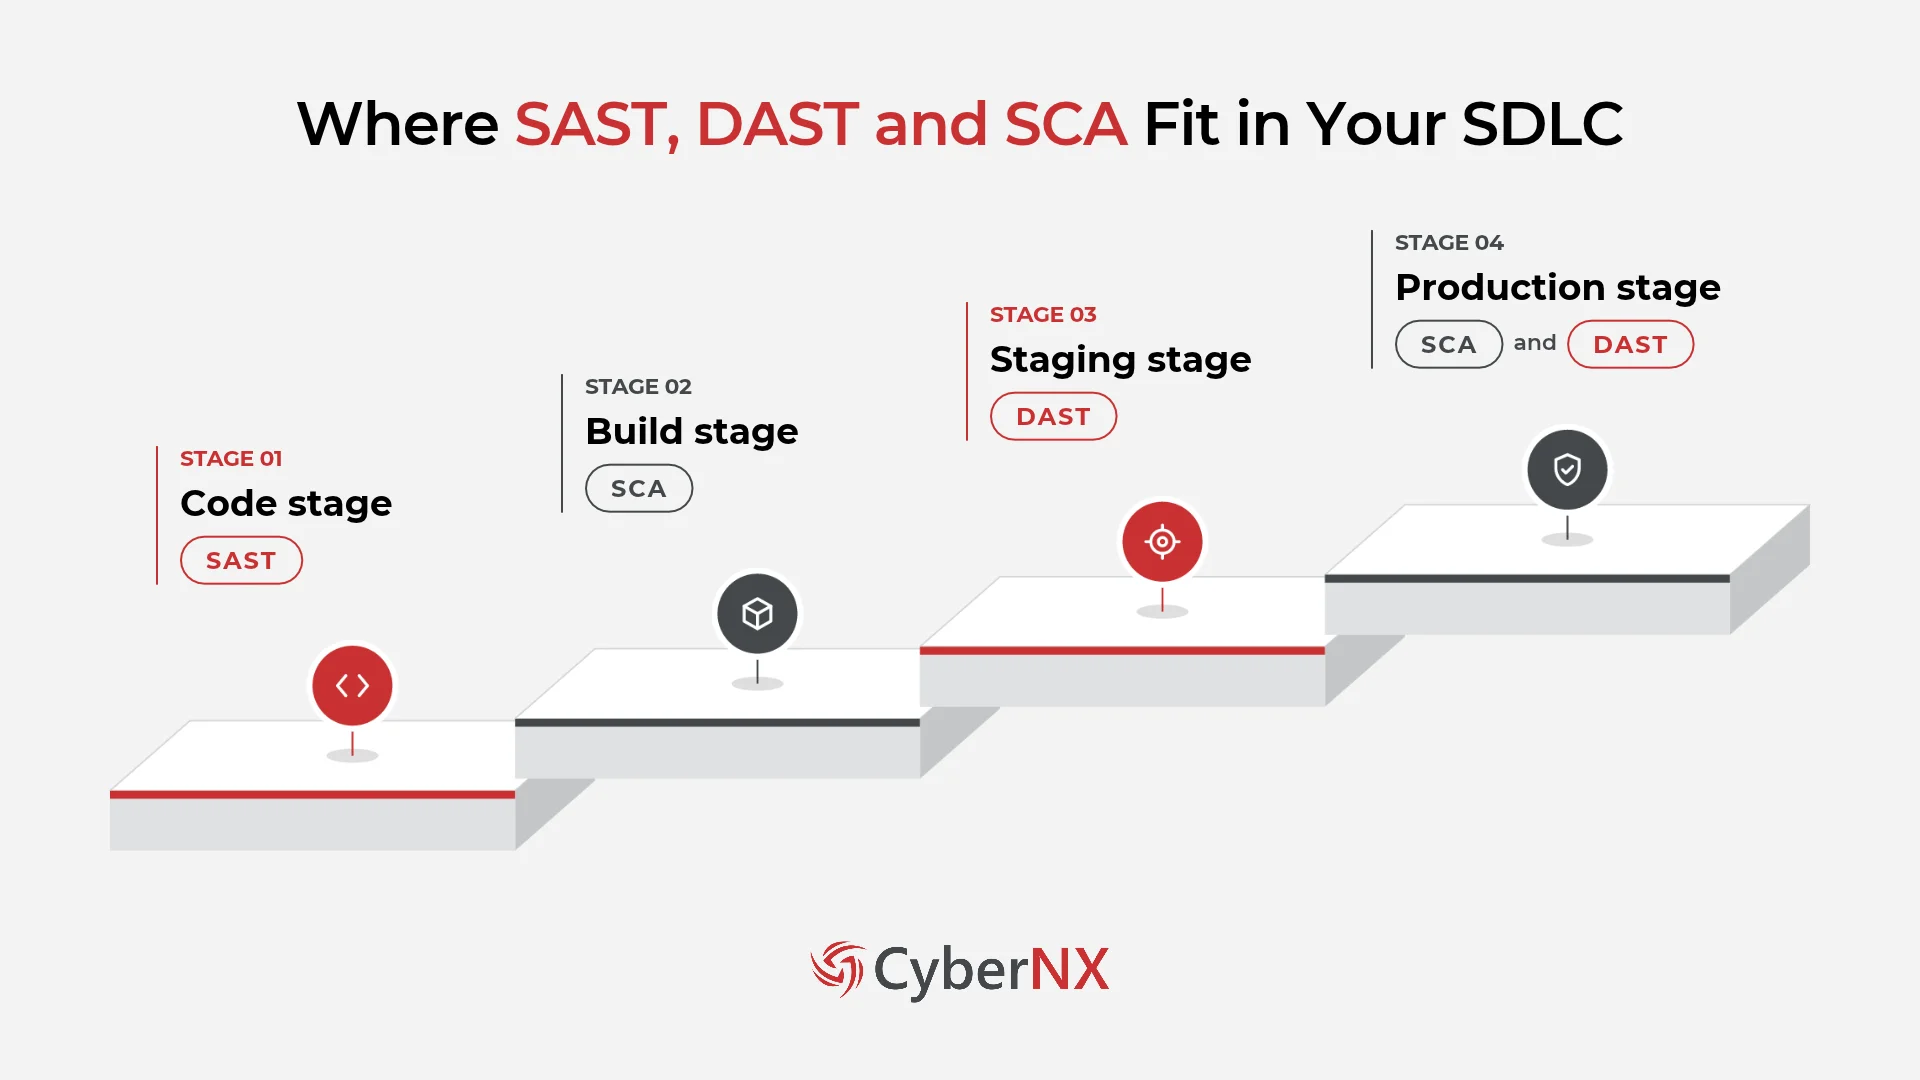
Knowing the differences is only half the job. Real value comes from timing each test well. Here is how we map them across the software development lifecycle (SDLC).
1. Commit and code stage
Run SAST on every pull request or commit. Developers then get feedback while the code is still fresh in their minds. Integrating SAST into the IDE shortens the fix cycle even further.
2. Build and dependency stage
Trigger SCA during every build to stop risky components before they ship. New vulnerabilities are disclosed daily, so a clean build today may fail tomorrow. Continuous SCA monitoring after release closes that window. You can also set build policies that block packages with critical, reachable vulnerabilities.
3. Staging and production
Run DAST against staging once the application is fully assembled. Use quick scans for routine deployments and deeper scans for major releases. Repeat DAST after significant configuration or infrastructure changes too.
Why scanners alone still leave gaps
Running all three tests gives you broad, layered coverage. Yet even a mature toolchain cannot understand what your application is meant to do.
Business logic needs human context
Tools recognise patterns, not purpose. They will not notice a discount API that lets users apply one coupon twice. Nor will they spot an approval workflow that quietly skips a required sign-off. Weaknesses like these need a reviewer who understands the intended behaviour.
Findings need expert triage
Automated scans can generate hundreds of alerts in a single release. Without proper triage, developers waste time on false positives and miss real risks. An experienced reviewer separates exploitable issues from harmless ones and explains each fix clearly.
Tool coverage varies by stack
Many scanners support popular languages well but struggle with legacy or niche frameworks. Custom wrappers, code generators and in-house libraries can also confuse automated analysis. A manual review fills these coverage gaps across your critical modules.
This is where manual secure code review complements SAST, DAST and SCA.
A structured review helps ensure that critical areas of your application are not overlooked. Use our Secure Code Review Checklist to understand the key areas reviewers should examine during an assessment.
Final thoughts
SAST vs DAST vs SCA is not a contest with a single winner. SAST secures the code you write, while SCA secures the components you borrow. DAST then validates how everything behaves once it goes live.
Still, scanners see patterns, so logic weaknesses and false positives need expert eyes. That is exactly where our Secure Code Review service helps. Our specialists pair automated analysis with manual, line-by-line review of your critical code. We validate every finding and give your developers clear, practical fixes.
Want to know what your scanners are missing? Talk to our team for detailed assessment.
SAST vs DAST vs SCA FAQs
Is IAST a replacement for SAST and DAST?
Not quite. Interactive Application Security Testing (IAST) places sensors inside a running application. It combines code visibility with runtime context, which cuts down false positives. However, it only tests code paths that your test traffic actually reaches. Most teams use it alongside SAST and DAST, not instead of them.
Which test should we start with on a limited budget?
Start with SCA if your applications rely heavily on open source. It is quick to set up and covers a large share of your codebase. Add SAST next, then bring in DAST as your release process matures.
Can SAST tools reliably review AI-generated code?
SAST scans AI-generated code like any other code. It still catches familiar patterns such as injection risks and exposed secrets. However, AI assistants can produce code that looks correct yet behaves insecurely. We recommend human review for high-risk modules like authentication and payments.