If you are comparing SAST vs SCA, you have probably heard that you need both. That is true, but it does not explain why. Without the reasoning, it is hard to plan budgets, tools or pipeline changes.
So let us keep it simple. Your application has code you wrote and code you imported. Each part carries a different kind of risk, and each needs a different kind of scan. In this blog, we walk you through what each approach does, where they differ and how to run them together in a practical way.
SAST vs SCA: The simple view
Before we go deeper, here is the short version.
SAST stands for static application security testing. It reviews the source code your developers write, without running the application. SCA stands for software composition analysis. It inspects the open-source and third-party components your application depends on.
So, is SCA the same as SAST? No. The easiest way to separate them is ownership. SAST checks the code you wrote, and SCA checks the code you consume.
Let us make that clearer. Your developers write the login logic, payment flows and business rules. Those are your own files, and SAST reviews them line by line. The same application also pulls in frameworks, libraries and packages from other people. Your team did not write them, but they still run inside your product. SCA identifies those components and checks their versions against known vulnerabilities.
Both reduce risk, but they look at different places.
How SAST works
SAST works on the code your own developers write, usually before anyone runs it.
It reads your source code, bytecode or binaries. It uses rules, data flow analysis and taint tracking. These methods follow untrusted input from where it enters to where it is used. A good result points to the exact file, function and line number.
Typical findings include:
- SQL injection
- Cross-site scripting (XSS)
- Buffer overflows
- Hardcoded credentials
One limit is worth remembering. SAST is language specific. A Java setup will not scan your Python or Go services, so each major language needs its own rules and tuning.
How SCA works
SCA works on everything your team did not write but still import.
It lists every library and package in your application, including dependencies you never chose directly. It reads files such as package.json, pom.xml and requirements.txt. Then it compares each version against databases like the NVD.
Beyond security, SCA reports licence risks and supports SBOM creation. In most cases, it does not need your source code.
Where SAST and SCA findings differ
Here is a clear comparison, since their findings rarely overlap.
| Factor | SAST | SCA |
| Full form | Static application security testing | Software composition analysis |
| What it examines | Proprietary code your team writes | Open-source and third-party components |
| Main question | Is the code we wrote vulnerable? | Are the components we imported vulnerable? |
| Typical findings | Injection flaws, XSS, weak cryptography, hardcoded secrets | Known CVEs, outdated packages, licence risks |
| Input needed | Source code, bytecode or binaries | Manifests, lock files, container images, build artefacts |
| Usual fix | Developers change the code | Upgrade or replace the component |
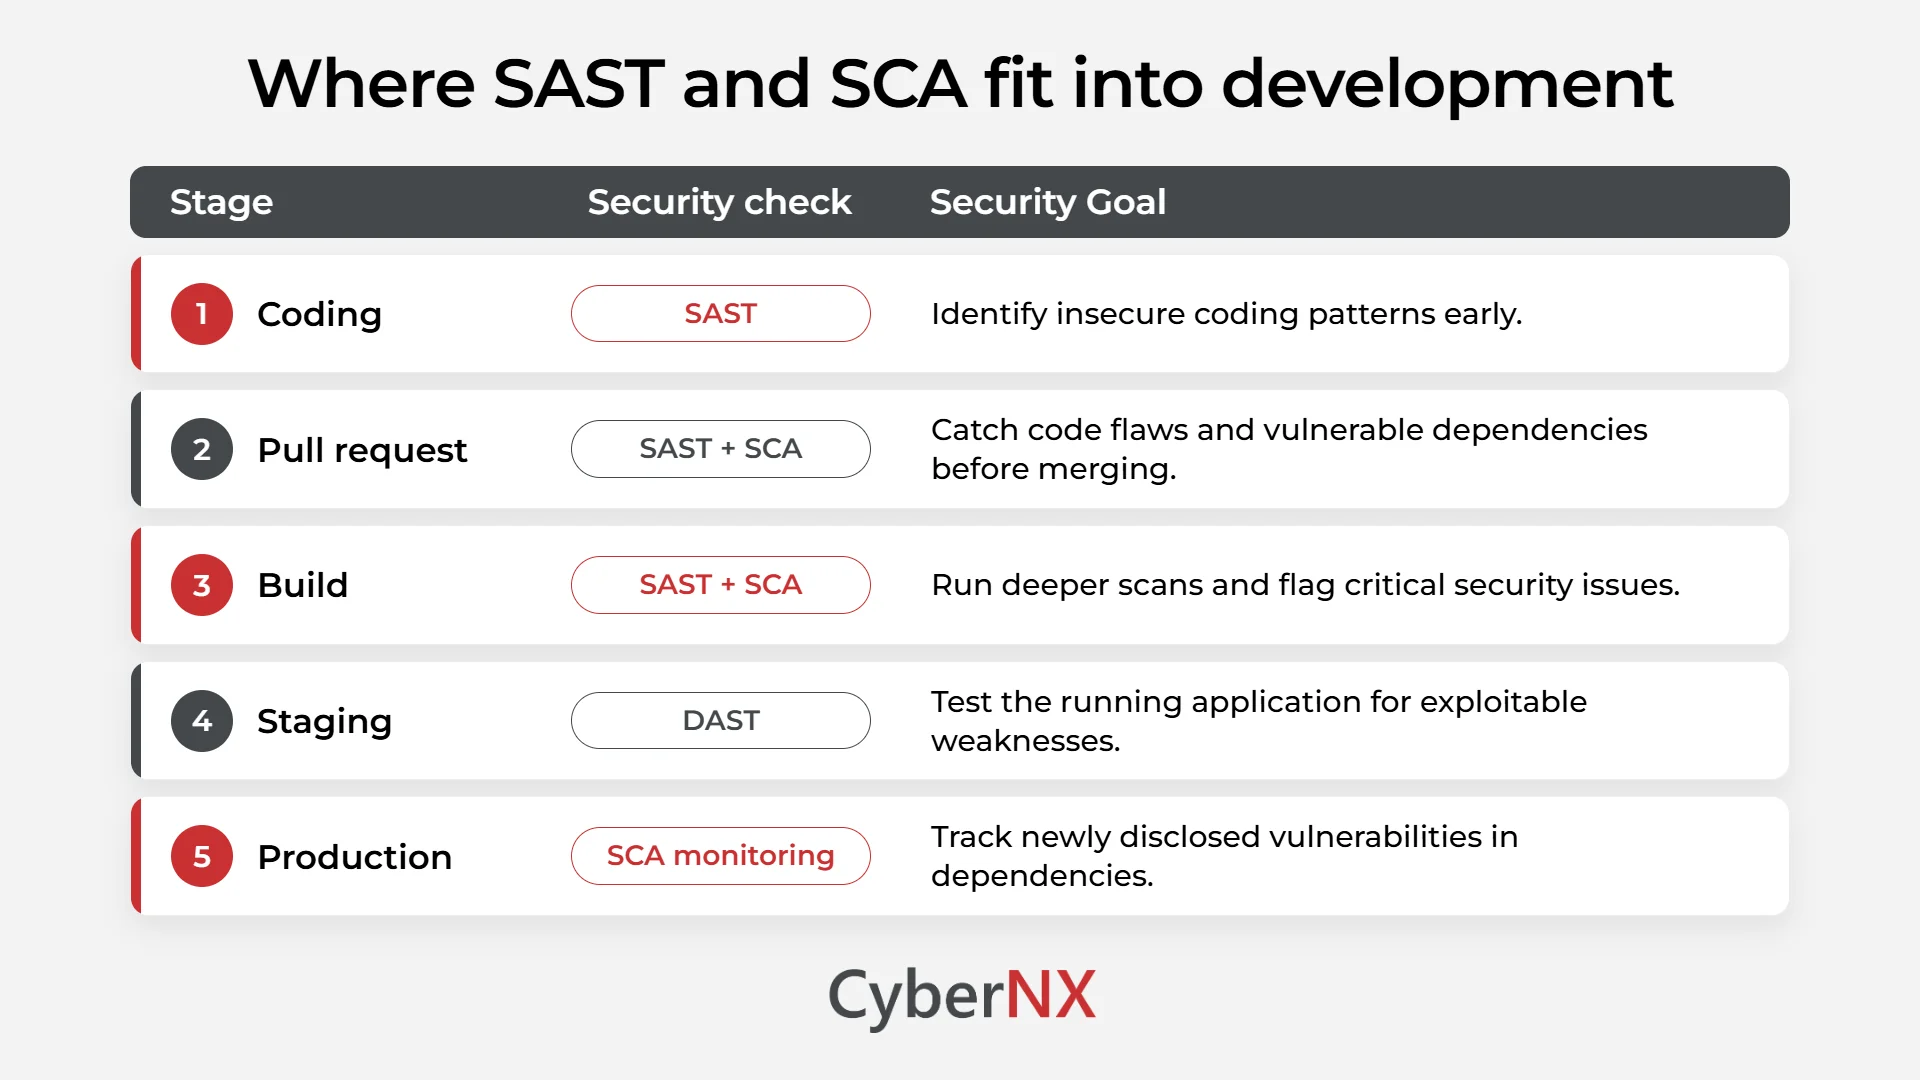
| Best stage | Coding and pull requests | Build stage and monitoring after release |
| Extra value | Secure coding evidence | Licence compliance and SBOM support |
| Blind spot | Dependency CVEs and runtime behaviour | Custom logic flaws and runtime behaviour |
So, what do the differences between SAST and SCA vulnerabilities look like in practice? Take Log4Shell, tracked as CVE-2021-44228, which scored 10.0 on the CVSS scale. The flaw sat inside the Apache Log4j library, not in the application’s own code. A SAST scan would not name the vulnerable version. SCA would find it in your dependency tree.
Now reverse the situation. A SQL injection flaw in your custom login page lives in your code. SCA will not see it, but SAST will.
SAST vs SCA: Which one should you start with?
Most applications benefit from both, but which one you start with depends on your security needs.
Choose SAST first when your value sits in custom logic, such as authentication, payments or API authorisation. Choose SCA first when your application leans on open-source packages, SDKs or container images. SCA often gives faster visibility, because it only needs your manifests.
NIST SP 800-218 supports using both. It helps teams check their own code and assess the third-party components they use. A good approach is to start with one tool and bring in the other soon after.
You may also add DAST, which tests the running application. SAST and SCA do not execute anything, so DAST confirms what is actually exposed after deployment.
Mistakes to avoid when running both
Buying the tools is the easy part. Using them well takes more care.
- Treating severity scores as the final priority: A critical CVE in an internet-facing service should move ahead of the same CVE in an internal test tool.
- Not adjusting scan rules: Untuned SAST produces false positives, and developers soon stop trusting the results.
- Scanning only during builds: New vulnerabilities can appear after release, so keep checking dependencies.
- Ignoring code usage: A flagged library may contain a vulnerable function that the application never uses.
- Using separate dashboards: Different severity ratings across tools make it harder to review and prioritise findings.
Where SAST and SCA fit into development
This simple view shows when each scan works best across your delivery pipeline.
Final thoughts on SAST vs SCA
SAST vs SCA is not a choice between two tools. It is a decision about coverage. SAST protects what you build, and SCA protects what you borrow. Together, they show your real exposure.
Knowing this is one thing. Running it well across many teams and pipelines is another.
At CyberNX, we help you with exactly that with our Secure Code Services. Our cybersecurity experts review your code, test them for weaknesses and guide your developers through practical fixes. We also help you build security checks into your CI/CD workflow, so issues are found before release. If you want a clear picture of your application risk, you can reach out to us.
SCA vs SAST FAQs
What do SCA and SAST stand for?
SAST means static application security testing. SCA means software composition analysis.
Is SCA the same as SAST?
No. They check different things. SAST looks at the code your team writes, while SCA looks at the open-source and third-party components you import. A vulnerability in one will often be invisible to the other. That is why the two tools work as partners and not as replacements.
Does SAST detect open-source vulnerabilities?
No. SAST does not keep an inventory of third-party packages or their versions.
Which should we adopt first, SAST or SCA?
It depends on what your application is made of. If it leans heavily on open-source packages, SCA is a sensible start. It needs only your manifest files, so you get visibility quickly. If your main risk sits in custom logic, such as authentication, payments or API authorisation, begin with SAST. In both cases, plan to add the second tool soon after. Running only one leaves a predictable gap.
Can SAST and SCA replace DAST?
No. SAST and SCA work before or during the build, and neither runs your application. DAST tests the running application, so it shows how the system behaves once it is deployed and configured. Most mature programmes use all three at different stages.
How often should we run SCA scans?
Continuously. New CVEs are disclosed after release, so a clean result today may not hold next month. A practical approach is to run quick checks on every pull request and deeper scans at build. Then keep monitoring your deployed applications, so you hear about newly disclosed issues without waiting for the next release.