Running endpoint detection on one tool, threat intelligence on another and identity monitoring on a third has disadvantages. This is because every tool has its own console and resultant alerts. Somewhere in that noise, there is a chance that you may miss real threat.
The CrowdStrike Falcon platform was built to fix exactly that. One lightweight agent on each device. One cloud-based console where your team sees everything and responds to it. If you are evaluating Falcon or trying to explain it to a board that keeps asking why you need yet another security investment, here is what you need to know.
What is the CrowdStrike Falcon platform?
The Falcon platform is a cloud-native cybersecurity platform built around a single agent called the Falcon sensor. You install it on each device. It watches everything – process activity, user behavior, network connections, file changes – and streams that telemetry to CrowdStrike’s cloud for analysis.
The platform covers endpoint detection and response (EDR), identity security, cloud workload protection, browser security and next-generation Security Information and Event Management (SIEM). All of it runs through one sensor and one console.
How it works
Most organisations run multiple agents on each device because their tools do not talk to each other. The Falcon sensor handles data collection for every capability the platform offers, so there is no agent sprawl and no performance drag.
That telemetry feeds into CrowdStrike’s Threat Graph, which processes trillions of events each week from millions of endpoints globally. When a new attack technique appears in one customer environment, every other customer benefits from that detection logic within minutes.
At Fal.Con 2026, CrowdStrike took this further with coordinated multi-agent investigations – AI agents working simultaneously across endpoint, identity, SaaS, cloud and network to complete in minutes what previously took hours. With the average adversary breakout time now at 29 minutes, that speed is no longer optional.
Why traditional antivirus falls short
According to the CrowdStrike 2026 Global Threat Report, 82% of detections in 2025 involved no malware at all. Attackers are using stolen credentials, legitimate admin tools and living-off-the-land techniques that leave no malicious file to scan. Increasingly, they are also targeting the browser session itself – through phishing, session hijacking and adversary-in-the-middle attacks that bypass controls which stop at the endpoint or the login event.
Traditional antivirus matches files against known signatures. If the signature is not on the list, the file passes. Falcon watches behaviour instead – what processes do, how users authenticate, how systems communicate. That is what makes it effective against the attacks that are happening now.
What are the different versions of CrowdStrike Falcon?
This is where buying conversations get complicated. Here is a clear breakdown of the four main versions.
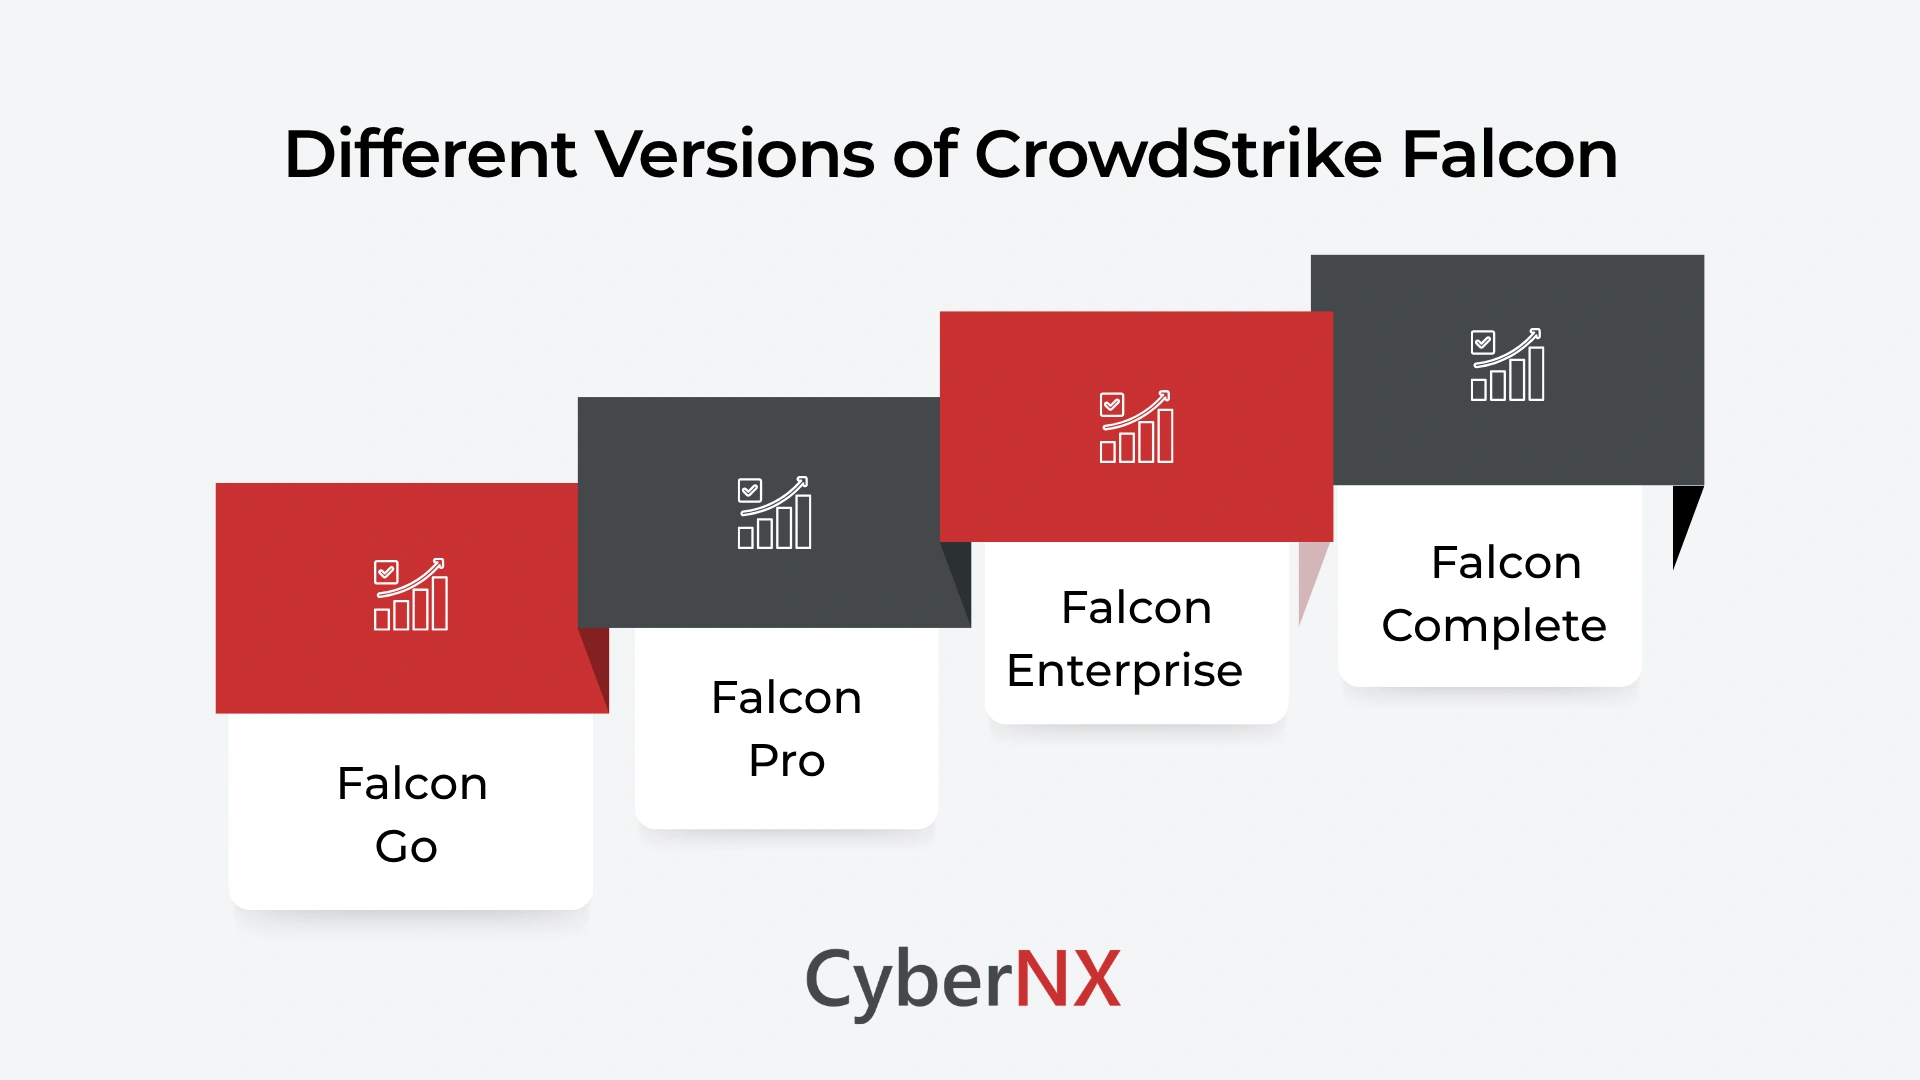
Falcon Go
Covers next-generation antivirus and device control. A significant step up from traditional antivirus, but without full EDR. Suitable for smaller teams getting started.
Falcon Pro
Adds full EDR through Falcon Insight XDR. Your analysts can investigate threats in detail and respond directly from the console. For organisations with a security team but no fully staffed SOC, this is often the practical starting point.
Falcon Enterprise
Includes XDR, identity threat detection and threat intelligence feeds. Built for teams with the internal capacity to investigate what the platform surfaces and act on it. The Spring 2026 release also added AI-native threat detection to uncover shadow AI and detect attacks on AI tools across endpoints, browser and SaaS – relevant if your teams are actively using GenAI applications.
Falcon Complete
This is the fully managed option. CrowdStrike’s own analysts monitor your environment 24/7, investigate alerts and respond to threats on your behalf. It includes a breach prevention warranty. For organisations without the headcount to run a round-the-clock Security Operations Centre (SOC), Falcon Complete removes that gap entirely. Our CrowdStrike MDR guide covers what the managed service includes in practice.
A newer addition worth noting: Falcon Secure Access extends the platform into the browser session – protecting access to SaaS apps, GenAI tools and unmanaged devices without requiring a separate tool.
If you are planning a deployment, our MDR implementation guide walks through sensor setup, policy configuration and integration steps. And if you are still deciding between managing security internally or going fully managed, our CrowdStrike MDR vs in-house SOC comparison can help.
The right fit depends on your team
The Falcon platform is not a feature upgrade on what you already have. It is a different category of security – one sensor, one console, cloud-scale intelligence and coverage that now extends from the endpoint to the browser to the agentic SOC.
Which version fits your organisation depends on your team’s capacity to act on what the platform surfaces. CyberNX is a CrowdStrike services partner. We help organisations assess the right version, deploy it correctly and get measurable outcomes from day one.
Talk to our CrowdStrike consulting team and let’s work out what your environment needs.
CrowdStrike Falcon Platform FAQs
What is the CrowdStrike Falcon platform used for?
The Falcon platform protects organisations against threats across endpoints, identities, cloud workloads and browser sessions. It detects threats using behavioural AI and adversary intelligence rather than file signatures, which makes it effective against modern attacks that use no malware at all. Security teams use it to investigate incidents, respond to threats and monitor their environment continuously – all from a single console.
What are the different versions of CrowdStrike Falcon?
CrowdStrike offers four main versions. Falcon Go covers next-generation antivirus. Falcon Pro adds full EDR. Falcon Enterprise includes XDR, identity protection and threat intelligence for SOC-capable teams. Falcon Complete is the fully managed service where CrowdStrike’s analysts monitor and respond on your behalf, backed by a breach prevention warranty.
Is the Falcon platform suitable for mid-sized organisations?
Yes. The platform scales from growing teams on Falcon Pro up to large enterprises on Falcon Enterprise or Falcon Complete. Mid-sized organisations without a full internal SOC often find Falcon Complete the most practical option – it removes the need to hire and retain specialist analysts for 24/7 coverage.
How does Falcon differ from traditional antivirus?
Traditional antivirus scans files against a list of known malicious signatures. Falcon watches behaviour instead. It monitors what processes do, how users authenticate and how systems communicate. This catches threats that leave no malicious file behind – including credential-based attacks, fileless techniques and hands-on-keyboard intrusions by human attackers.