If you talk to three SAST vendors about AI, you will hear three different views. The first will say that its tool finds tricky logic flaws that standard rules cannot detect. The second will say that its tool filters out false alarms before they reach your developers. And the third will say that its tool writes the fix for you. Yet all three describe their product as “AI-powered”.
That is where buying a SAST tool becomes tricky. When the same label has different meanings for different vendors, it becomes difficult to compare the tools. And one wrong choice could leave you with months of scan results full of false positives, while your developers gradually lose trust in the reports.
The good news is that you can find out what each tool actually does. Our team has hands-on experience with these tools and has used them while testing client applications. So, here we share our insights on top AI SAST tools. Let’s begin.
What counts as an AI SAST tool?
SAST stands for static application security testing. It analyses your source code without running it, looking for flaws such as injection paths, unsafe data handling and hard-coded secrets. Because it works on code at rest, it can run early, inside the developer’s editor or on a pull request.
An AI SAST tool adds AI to that process. So how is AI SAST different from traditional SAST? A traditional scanner matches your code against a fixed set of rules and reports every match. That approach produces many false positives, and it misses flaws that no pattern can describe, such as a missing permission check. An AI SAST tool keeps the scanning foundation and adds judgement on top. It reads the code around a finding, decides whether the flaw is reachable and can draft a fix.
Not every tool does all of this. Some use AI deep inside detection. Others use it only to sort results or suggest patches. You will also see two labels.
- AI-powered SAST adds AI to an existing rule engine.
- AI-native SAST builds detection around model reasoning from the start.
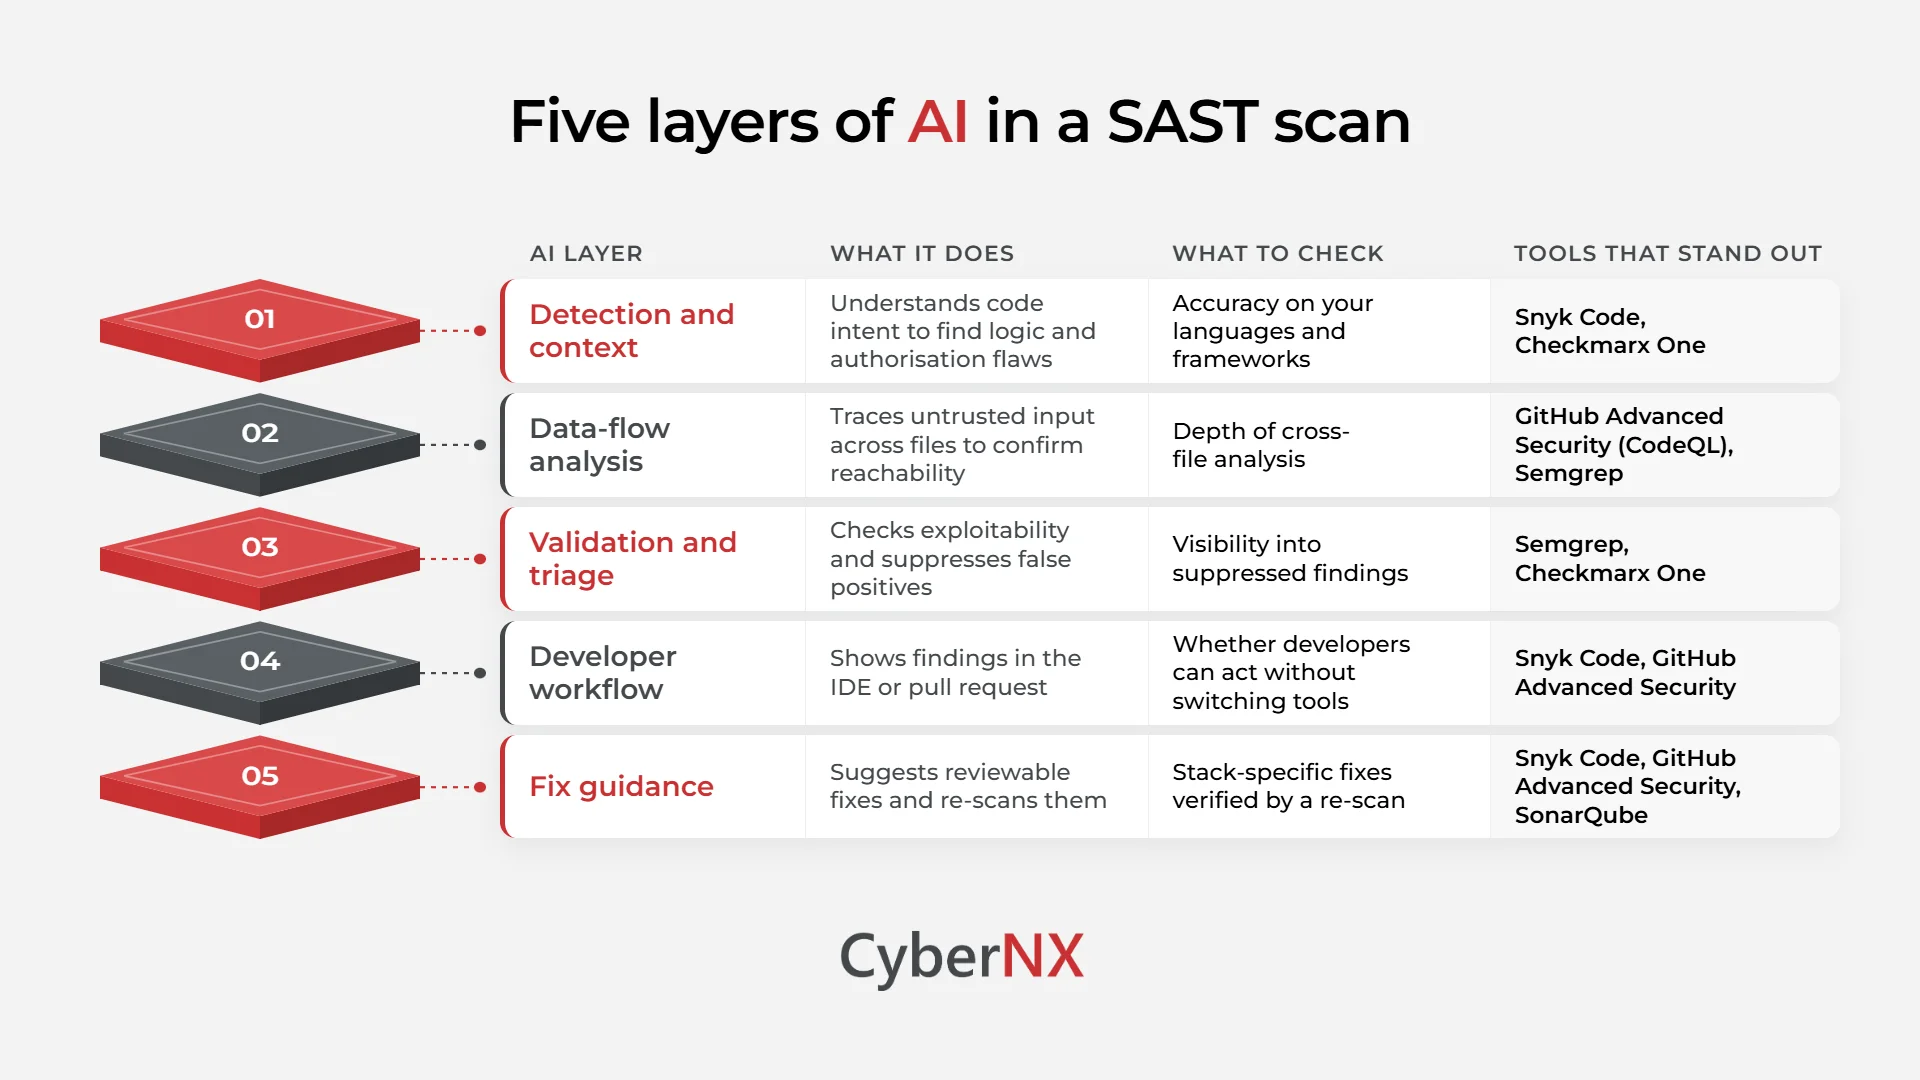
Neither is automatically better, and the infographic below shows where AI can sit in a scan.
Five places AI shows up in a SAST scan
The first three layers change the quality of the findings. The last two change how easy the tool is to live with. Both matter, but they are not the same purchase.
The 5 best AI SAST tools
These tools are not ranked. Each one fits a different kind of team. Features and pricing change quickly in this market, so confirm current details with each vendor before you buy.
1. Snyk Code
Snyk Code is built for speed. Its DeepCode AI engine combines symbolic analysis with generative AI, and it is designed to flag problems while a developer is still typing.
- Real-time scanning in the IDE and on pull requests keeps feedback close to the code.
- AI fix suggestions are checked by re-scanning, so a patch does not quietly add a new flaw.
- Snyk sits inside a wider platform that also covers open-source dependencies, containers and infrastructure as code.
- Reviewers note that default settings can be noisy, and that costs rise as developer counts and modules grow. Benchmark results for its detection depth also vary, so test it on your own code.
- A free plan exists with a monthly cap on Snyk Code tests for private projects.
Best for: Developer-led teams that want fast, in-editor feedback and self-serve adoption.
2. Semgrep
Semgrep started as a fast, rule-based scanner whose rules look like the code they match. AI now sits on top of that base, which makes it one of the more transparent AI SAST solutions.
- Semgrep Assistant uses AI to triage findings, filter likely false positives and suggest remediation.
- The paid engine adds cross-file analysis, so it can follow data across functions.
- Your engineers can read, write and version their own rules instead of trusting a black box.
- The open-source Community Edition is free, and the managed platform has had a free tier for small teams.
- Custom rule libraries need upkeep, and programme-level reporting is lighter than in enterprise platforms.
Best for: Engineering-led teams that want fast, customisable scanning and are happy to maintain their own rules.
3. Checkmarx One
Checkmarx One packages a mature enterprise SAST engine into a cloud platform and layers AI assistance on top. Its reputation rests on breadth and control.
- It covers a long list of languages and frameworks, which helps with older and unusual codebases.
- Queries are tunable, so skilled teams can decide exactly what gets flagged.
- AI helps with triage, plain-language explanations and remediation guidance.
- Setup and tuning need real expertise, and licensing sits at the premium end. It can feel heavy for a small team.
Best for: Large enterprises with complex application portfolios and dedicated AppSec staff.
4. GitHub Advanced Security
GitHub Advanced Security puts static analysis where much of the world’s code already lives. CodeQL treats code as data you can query, and Copilot Autofix drafts fixes inside the pull request.
- Scanning arrives as a repository setting, so adoption friction is very low for GitHub teams.
- CodeQL gives deep semantic analysis, though it is a query engine and not an AI detector.
- Copilot Autofix turns findings into reviewable changes in the same screen.
- CodeQL is free for public repositories. Private repositories need a paid licence.
- Value drops if your code is split across platforms, and reporting is basic next to dedicated AppSec tools.
Best for: Organisations that standardise on GitHub and want scanning without adding another vendor.
5. SonarQube
SonarQube reaches security from the code-quality side, where it already sits in many engineering teams. That installed base is its main advantage.
- AI CodeFix drafts remediation suggestions, and AI Code Assurance helps teams hold AI-written code to defined quality and security bars.
- Security findings appear in a dashboard developers already check, so they actually get read.
- The Community Build is free and self-hosted, and cloud options exist.
- Pure security depth trails dedicated SAST engines on complex vulnerability classes. Self-hosted setups also leave server upkeep with your team.
Best for: Teams that already run SonarQube for quality and want security checks in the same workflow.
More AI SAST tools worth knowing
If you’re still evaluating your options, consider these additional AI SAST tools before finalising your shortlist:
- Veracode: Veracode Fix drafts AI-assisted remediation, and governance and compliance reporting are its strengths.
- GitLab Advanced SAST: Cross-file analysis and AI explanations inside the merge request, best for GitLab teams.
- Cycode: Combines rule-based and AI reasoning inside a wider application security platform.
- Qwiet AI: Reasons over a code property graph to separate reachable flaws from theoretical ones.
- DryRun Security and Corgea: Newer AI-native tools, one centred on reviewing pull requests and the other on automated fix pull requests.
AI SAST tools at a glance
| Tool | Where AI helps most | AI in detection | AI triage / validation | In-workflow (IDE / PR) | AI fix guidance | Free option | Best for |
| Snyk Code | Real-time detection and verified fixes | ✅ | Partial | ✅ | ✅ | Yes, limited tests | Developer-led teams |
| Semgrep | AI triage on top of transparent rules | Partial | ✅ | ✅ | ✅ | Yes, open source plus small-team tier | Engineering-led teams that write rules |
| Checkmarx One | AI-assisted triage on a deep enterprise engine | Partial | Partial | ✅ | ✅ | No | Large enterprises |
| GitHub Advanced Security | Autofix inside the pull request | ❌ | ❌ | ✅ | ✅ | Public repositories only | GitHub-centred organisations |
| SonarQube | AI fixes and AI-code checks in a quality workflow | ❌ | ❌ | ✅ | ✅ | Yes, Community Build | Teams already using SonarQube |
Matching a tool to your problem
Pick the one problem you most want AI to solve, because each tool is strongest in a different place.
- Too many false alarms: Semgrep and Checkmarx One put their AI into triage and validation.
- Developers own the fixes: Snyk Code and GitHub Advanced Security work in the IDE and pull request.
- Control and transparent rules: Semgrep.
- Large, regulated portfolios: Checkmarx One.
- Already on SonarQube: Add security checks there first.
- No budget: Start with the free options above.
Do not decide from a demo alone. Run a short trial:
- Pick one or two real repositories, including an older, complex one.
- Give each tool the same scope and seed it with known vulnerabilities.
- Review a sample of findings by hand.
- Count false positives, missed vulnerabilities and setup hours.
- Check whether the fixes fit your framework and developers accept them.
Two weeks is usually enough. Your own results will tell you more than any vendor figure.
Your next step with AI SAST tools
AI will not fix a poor testing process on its own, but in the right place it can find vulnerabilities older scanners miss and save your developers hours of triage. Test that claim on your own code before you buy.
Running SAST well takes more than a licence. At CyberNX, we help you shortlist tools, run trials on your applications, fix what the scans find and connect SAST to your CI/CD pipeline so issues are found before release.
SAST reads your code but cannot see how the running application behaves, so we pair it with DAST and our secure code review service. Our engineers read your source line by line and find the logic errors scanners miss. Together, they give you a full view of your application risk.
Get in touch with us to start.
AI SAST Tools FAQs
Which is the best AI SAST tool?
There is no single best tool. Snyk Code suits developer-led teams that want fast IDE feedback. Semgrep suits teams that want transparent, customisable rules. Checkmarx One suits large enterprises. GitHub Advanced Security suits GitHub-centred teams. SonarQube suits teams that already use it for code quality. Trial two or three on your own code.
Are there free AI SAST tools?
Yes. Semgrep Community Edition, the SonarQube Community Build and CodeQL for public repositories are free. Snyk also offers a free plan with a monthly test cap. Free tiers usually limit AI features, private repositories or scan volume, so check the terms.
Can AI SAST replace manual secure code review?
No. AI SAST gives fast, repeatable coverage on every commit. A human reviewer goes deeper into business logic and complex flaws. Most mature teams use both, with SAST for regular checks and manual review for critical applications.
Do we still need DAST and SCA if we use AI SAST?
Yes. SAST checks the code you write. DAST tests the running application from the outside, and SCA checks the open-source code you import. Together they give the fullest picture.