Financial services, without a doubt, is a highly regulated sector today. This is because of the growing concern around cybersecurity. A decade ago, software supply-chain transparency was almost non-existent. Companies investigated third-party libraries or dependencies only for compliance purposes.
In April 2024, the Reserve Bank of India established a strong governance and control regime for banks, NBFCs, and other regulated entities. But lately, there has been a major shift. On 31 July 2026, it issued seven parallel Cybersecurity, Technology: Risk, Resilience and Assurance Framework Directions – one for each entity class – commercial banks, small finance banks, payments banks, urban co-operative banks, all-India financial institutions, NBFCs and credit information companies.
All came into force immediately, repealing earlier cyber and IT-governance instructions. This changes cybersecurity from a technical compliance function into a board-driven governance and risk management responsibility.
In this blog, find out how SBOM Aligned RBI Master Directions on IT Governance and Cybersecurity opens opportunities to enhance transparency, resilience and compliance maturity.
Why governance, risk and software-supply-chain discipline matter
If you are leading cybersecurity in a bank or a fintech company, you already know how software ecosystems are expanding rapidly. There’s third-party integrations, cloud services and open-source components. And you know this is complex because it introduces significant risks too.
When a vulnerability emerges within a software library or component, it can cascade across dependent systems. Without visibility into these relationships, institutions struggle to respond effectively.
In this context, an SBOM makes every application transparent, helping institutions identify inherited risks early. Plus, it helps in maintaining compliance with both CERT-In and RBI expectations.
RBI Master Directions on IT governance, risk, controls, and assurance
The RBI’s Directions collects years of scattered cybersecurity circulars and IT-governance instructions into a single framework per entity class. For commercial banks, this replaces the previous patchwork completely. For NBFCs, small finance banks, payments banks and other entity classes, dedicated parallel Directions apply from the same date.
The old flexibility of interpretation that existed across fragmented circulars has been narrowed – the 2026 framework tells regulated entities what to do, who is accountable and with what frequency.
1. Scope and applicability
Seven entity-class-specific Directions cover: scheduled commercial banks (excluding regional rural banks), small finance banks, payments banks, urban co-operative banks, all-India financial institutions (EXIM, NABARD, NaBFID, NHB, SIDBI), NBFCs (across layers) and credit information companies.
Every class now has its own binding cybersecurity framework. A single baseline applies within each class, there is no longer room for tier-based interpretive flexibility on cybersecurity obligations.
2. Key requirements: governance, controls, and assurance
The 2026 Directions go beyond governance paperwork. Boards must give annual approval to IT, cybersecurity and business continuity strategies, with specified authority and reporting structures.
Commercial banks must conduct vulnerability assessments every six months, annual penetration tests for critical internet-facing systems, and half-yearly disaster recovery drills. Cyber incidents must be reported on the DAKSH platform within six hours of detection.
3. Implications for the software supply chain
The 2026 Directions remove any ambiguity that might have been present before. With explicit requirements around vendor due diligence, audit rights and supply chain risk management, SBOM is the expected evidence.
Vendors supporting regulated entities must now accommodate contractual audit rights and regulatory access clauses, allowing the RBI to reach through a regulated entity to its technology suppliers. An up-to-date SBOM with vendor-supplied components is the most direct way to satisfy these obligations.
What SBOM brings to the table
The RBI’s November 2024 circular made SBOM expectations explicit for the banking ecosystem. The 2026 Directions go further by embedding software supply-chain risk management into the core governance framework for every regulated entity class.
Delve into our blog How to Meet RBI SBOM Compliance and Strengthen Your Software Supply Chain to know more.
SBOMs turn software management from a guessing game into a structured, measurable process. Instead of a black box, you get clarity-what runs, where it came from, and how safe it is.
Why financial institutions need SBOM
For banks and NBFCs, SBOMs shine a light on software supply-chain risks. They reveal hidden third-party and open-source parts that might carry vulnerabilities. They speed up incident response too – when something breaks, you instantly know what’s impacted. They also tighten vendor management, weaving transparency right into contracts and audits. On top of that, SBOMs prove regulatory readiness – evidence that the institution actually knows what software runs its systems.
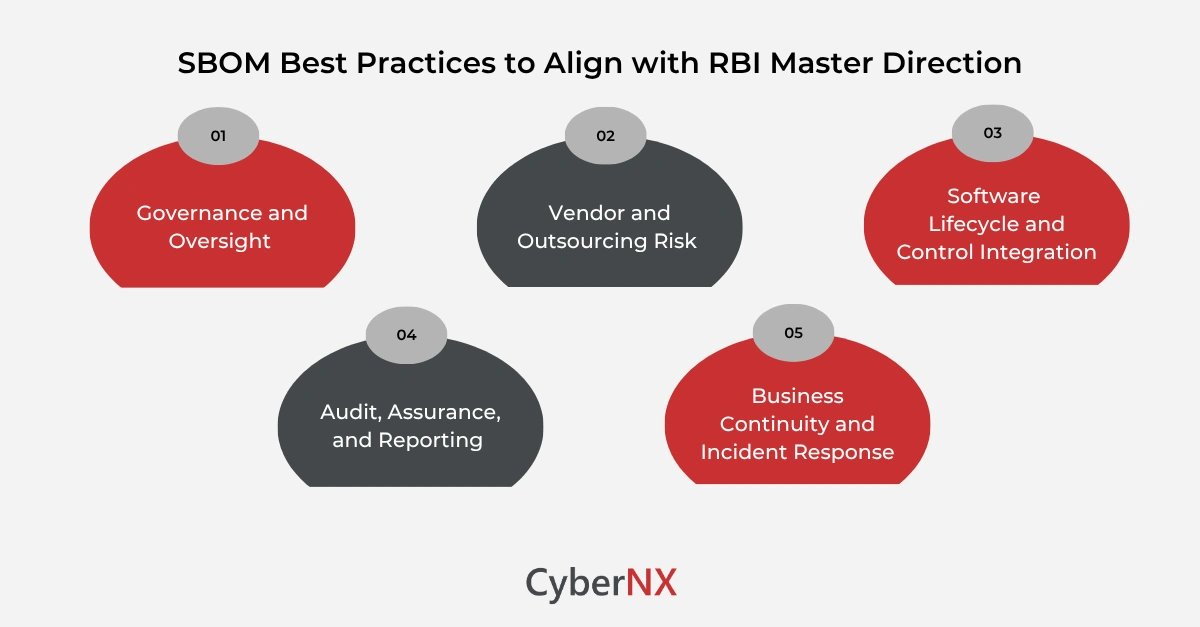
Aligning SBOM practices with the RBI Master Directions
Treating SBOM as a checkbox exercise misses the point. It has to be stitched into governance, risk, and compliance frameworks from top to bottom. Every function – from the boardroom to the audit desk – has a role in making it part of daily operations.
1. Governance and oversight
Boards and senior leaders should see SBOM as a live control tool for managing software supply-chain risk. It belongs in IT strategy reports and governance dashboards. Creating a dedicated Head of Software Supply-Chain Risk can keep oversight from slipping through the cracks. The 2026 Directions require boards to annually approve IT and cybersecurity strategies with specified authority structures. A dedicated owner for software supply-chain risk keeps accountability from slipping through the cracks between IT and compliance functions.
2. Vendor and outsourcing risk
Contracts must do the heavy lifting. Vendors should be obligated to produce and update SBOMs as part of their deliverables. Continuous monitoring of SBOM compliance then highlights weak spots before they turn into exposures.
3. Software lifecycle and control integration
SBOM generation should start early – right from software design – and continue through deployment. The 2026 Directions clearly require secure software development practices and cryptographic standards compliance. Integrating SBOM generation into the SDLC is the practical mechanism to demonstrate both. It also fits neatly with the bi-annual vulnerability assessments and annual penetration tests now mandated. Keeping it updated ensures change management tracks what’s new or risky in every release.
4. Audit, assurance, and reporting
Auditors, both internal and IS, need to verify the accuracy and completeness of SBOMs. They should check how SBOM data is created, stored, and fed into risk reports. Dashboards showing SBOM coverage can be a strong proof point during RBI inspections or internal reviews.
5. Business continuity and incident response
When a critical vulnerability surfaces, an SBOM lets institutions instantly pinpoint affected applications and vendors. That’s gold during a crisis-targeted patching, faster containment, and less downtime. The 2026 Directions mandate cyber incident reporting on the DAKSH platform within six hours of detection. That window leaves no time for manual component triage. Institutions with current SBOMs can immediately identify affected systems and communicate to the regulators.
Find additional practical practices our experts recommend for boardroom or an engineering review of SBOM in our blog SBOM Best Practices.
Common pitfalls and how to fix them
Many banks start strong but stumble later. Legacy systems often lack structured component data, and manual SBOM generation is slow and error prone. Automating it with certified tools keeps it current and accurate. Some vendors resist SBOM sharing – tight contracts solve that. The real key is to treat SBOM as a living document that evolves with system updates. Static SBOMs go stale fast.
A new pitfall worth noting is assuming the pre-2026 frameworks remain operative. The 31 July 2026 Directions repeal earlier cybersecurity and IT-governance instructions for every covered entity class – there is no transition period. Compliance programmes built on earlier circulars need an immediate gap assessment against the 2026 requirements, particularly around incident reporting, board approval obligations, vendor audit rights and the six-hour DAKSH reporting window.
Key takeaways for decision-makers
SBOM adoption aligns perfectly with the RBI’s goals for governance, control, and assurance. It shifts software visibility from an IT detail to a strategic governance lever. Early adopters will stand out – better compliance posture, reduced exposure, and smoother audits.
Partnering with cybersecurity specialists like CyberNX – who offer end-to-end SBOM solutions covering generation, management and regulatory mapping, makes rollout easier, embedding visibility into development, vendor contracts and audit workflows from day one.
Conclusion
For financial institutions under the RBI Master Directions, SBOM integration isn’t just smart – it’s necessary. It strengthens governance, sharpens vendor control, and provides verifiable compliance evidence. The 31 July 2026 framework makes the six-hour incident reporting legally binding across every entity class. An up-to-date, automated SBOM programme is the most direct path to meeting these obligations with evidence.
At CyberNX, our SBOM solutions give regulated entities the needed visibility – automating generation and mapping every component to your RBI, CERT-In and SEBI obligations. We embed SBOM into your development pipeline, vendor contracts and IS audit programme so you are not confused when it matters the most. Talk to our team today and see how fast you can move from zero visibility to full compliance posture.
SBOM aligned RBI Master Directions on IT governance and cybersecurity FAQs
Does the RBI Cybersecurity Directions 2026 explicitly mandate SBOM generation?
The RBI’s November 2024 circular made SBOM expectations explicit for the banking ecosystem. The 2026 Directions go further by inserting software supply-chain risk management, vendor audit rights and secure software development into legally binding obligations for every entity class. SBOM is the practical mechanism regulated entities use to prove compliance with all three.
Which SBOM formats are accepted under Indian cybersecurity frameworks?
CERT-In recommends SPDX and CycloneDX as standard formats. SPDX is ideal for license and compliance tracking, while CycloneDX focuses on security and vulnerability management. Both ensure consistent, machine-readable software inventories.
Can financial institutions phase in SBOM adoption?
Yes. Start with critical systems, generate high-level SBOMs, and progressively extend to full dependency mapping and vendor integrations.
How does SBOM improve incident response?
An SBOM enables quick identification of affected systems when vulnerabilities surface, reducing investigation time and enhancing recovery efforts.