CBOM and QBOM are appearing in the same compliance conversations, often used as if they mean the same thing. They do not, and the difference has real consequences for how Indian firms plan their cryptographic security roadmap.
Both terms entered India’s regulatory vocabulary formally through CERT-In Technical Guidelines v2.0 in July 2025. Since then, the DST Task Force report of February 2026 has recommended that organisations mandate CBOM submission from vendors through procurement policy from FY2027-28, and RBI’s newly formed Q-SAFE committee has been tasked specifically with evaluating the financial sector’s cryptographic posture through a CBOM lens. The pressure is building from multiple directions at once.
Organisations that conflate the two – risk building the wrong inventory, missing the right deadline or starting a post-quantum migration without the baseline they actually need. This guide breaks down the QBOM vs CBOM difference – what each covers, how they connect and where to start.
What is a CBOM?
A Cryptographic Bill of Materials (CBOM) is a structured inventory of every cryptographic asset in a system. Think of it as a documented list of the security mechanisms protecting your data, and what each one is made of. A complete CBOM ideally documents:
- Algorithms in use: RSA, ECC, AES, SHA-256 and related variants
- Key sizes and parameters: RSA-2048 vs RSA-4096, for example
- Digital certificates: issuers, validity periods and linked services
- Cryptographic libraries and versions: OpenSSL, BouncyCastle and others
- Protocols: TLS versions, SSH configurations, signing mechanisms
What is a QBOM?
A Quantum Bill of Materials (QBOM) is a related but distinct inventory. While a CBOM documents cryptographic assets broadly, a QBOM is oriented around quantum-safe cryptography – covering quantum algorithms, quantum security protocols, quantum hardware elements, quantum software dependencies and the cryptographic components relevant to quantum readiness within an organisation’s systems.
Under the CERT-In Technical Guidelines v2.0, Section 8, QBOM and CBOM are defined as separate inventory categories. QBOM is not simply a filtered subset of a CBOM – CERT-In treats it as the inventory lens for organisations integrating, building or assessing quantum-related systems and their cryptographic posture in that context.
There is no standalone QBOM specification. CERT-In recommends using known formats like SPDX or CycloneDX for both. The practical difference between QBOM vs CBOM lies in scope and intent, which the next section explains.
QBOM vs CBOM: what’s actually different?
The QBOM vs CBOM distinction matters most when deciding what to build and in what order.
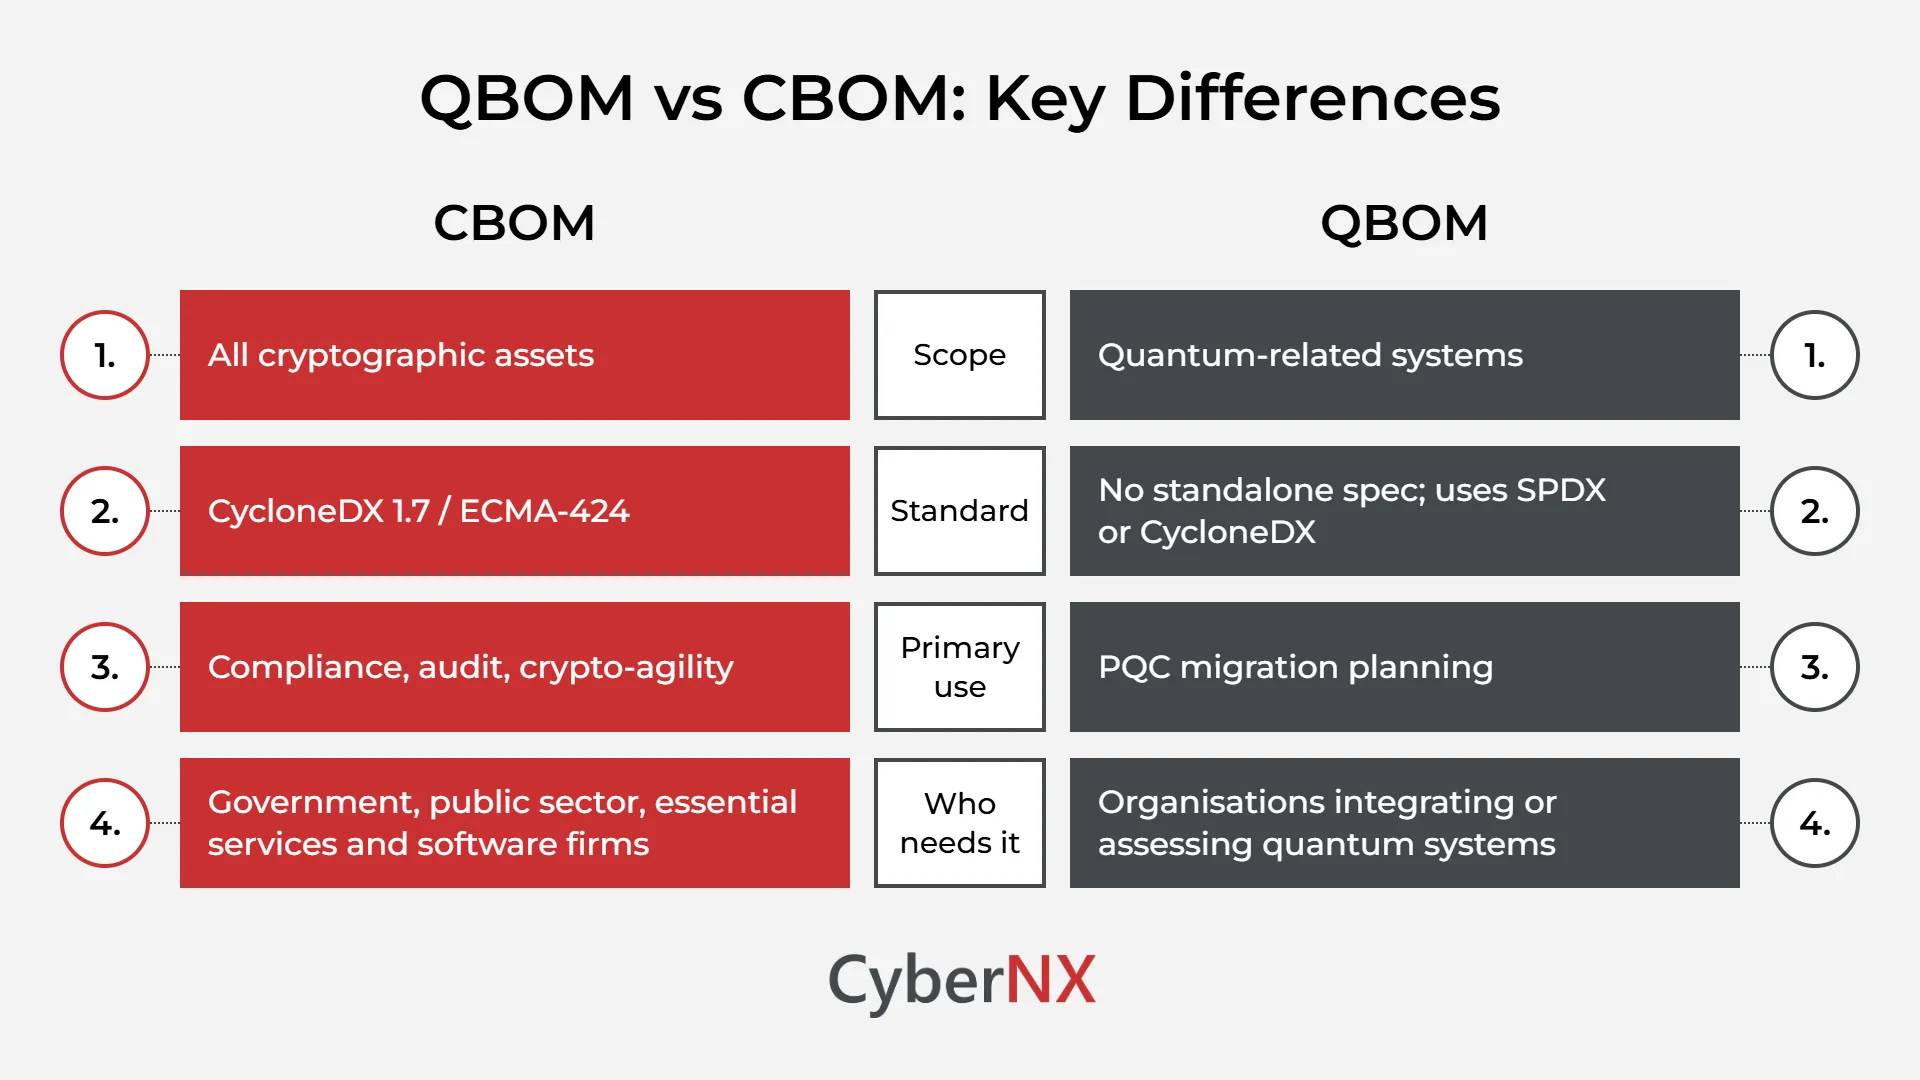
Here are the four dimensions where they diverge:
- Scope: A CBOM covers all cryptographic assets: algorithms, keys, certificates, libraries and protocols. A QBOM covers quantum-related components and the cryptographic assets relevant to quantum-safe readiness.
- Standard: Both CBOM and QBOM can be generated using recognised formats such as CycloneDX (now at version 1.7, codified as ECMA-424) or SPDX. There is no separate standalone QBOM specification.
- Primary use: CBOM satisfies audit, compliance and cryptographic visibility requirements. QBOM addresses quantum-safe readiness – mapping which components are relevant to post-quantum cryptography (PQC) planning and procurement.
- Who needs which: CERT-In’s guidelines specifically identify government bodies, public sector organisations, essential services and software-related organisations as the recommended scope for CBOM. QBOM is particularly relevant for organisations integrating, building or procuring quantum-related systems or planning a quantum-safe transition.
Why Indian enterprises can’t wait on this
The QBOM vs CBOM conversation is no longer theoretical for Indian organisations, it is a live compliance question.
The DST Task Force Report on the Quantum Safe Ecosystem in India (February 2026) set a phased sequence: build a cryptographic inventory, adopt crypto-agility, begin requesting CBOMs from vendors from FY 2026-27 and mandate CBOM submissions through procurement policy from FY 2027-28. For Critical Information Infrastructure – classified as urgent adopters – the roadmap targets full PQC adoption by December 2029.
The RBI’s Q-SAFE expert committee, constituted in May 2026, is tasked with evaluating the financial sector’s cryptographic inventory through a CBOM and assessing crypto-agility across banks and payment systems. RBI has not published a standalone quantum cryptography mandate yet – the Q-SAFE report is expected within six months of the committee’s first meeting. That nuance is important: CBOM is the active compliance obligation now; QBOM is the planning lens that follows.
For BFSI organisations, the QBOM vs CBOM programme must start now – data sensitivity windows are long and migration complexity across a typical bank’s stack is significant.
Building the QBOM vs CBOM together: the practical sequence
Both inventories share the same starting point. A workable sequence:
- Build your CBOM first: Scan network, code repositories, build artifacts and HSM/KMS integrations to document every cryptographic asset per application.
- Build your QBOM: Using the CBOM as a foundation, document your quantum-related components: quantum algorithms, quantum security frameworks, hardware dependencies and software elements interacting with quantum systems. Identify which cryptographic assets – particularly RSA, ECC, Diffie-Hellman and DSA – are vulnerable to quantum threats and need migration planning.
- Classify by data lifespan: Data needing confidentiality for five or more years is already exposed to harvest-now, decrypt-later attacks. Prioritise those assets first.
- Map to NIST PQC replacements: ML-KEM (FIPS 203) for key encapsulation and ML-DSA (FIPS 204) for digital signatures are the primary quantum-safe replacements for vulnerable algorithms.
Conclusion
The QBOM vs CBOM distinction is not about choosing one over the other. CBOM gives you visibility into all cryptographic assets – it is the foundation. QBOM addresses quantum-related systems and the cryptographic posture required for quantum-safe readiness. Both serve different purposes and, for many organisations, both will be needed as India’s quantum security expectations mature.
CyberNX offers CBOM solutions that help Indian firms document and continuously monitor every cryptographic asset across their systems and also cover QBOM and CBOM readiness, and audit-ready output aligned to CERT-In and RBI requirements. Talk to our experts and understand your cryptographic exposure before the deadline does it for you.
QBOM vs CBOM FAQs
Is QBOM the same as CBOM?
No. A CBOM is a full inventory of all cryptographic assets. A QBOM covers quantum-related components and the cryptographic elements relevant to quantum-safe readiness.
Which one does CERT-In require?
CERT-In Technical Guidelines v2.0 (July 2025) defines both in Section 8. For government bodies, public sector entities, essential services and software organisations, CERT-In uses mandatory language for relevant procurement, development and integration contexts. For others it is structured best-practice guidance. CBOM carries the more immediate weight given the DST Task Force timeline and RBI’s Q-SAFE work.
Does RBI require a QBOM?
Not yet. The Q-SAFE committee constituted in May 2026 is evaluating the financial sector through a CBOM. A QBOM-specific requirement may follow once the committee’s report is published.
When does CBOM become mandatory for Indian vendors?
The DST Task Force recommends mandatory CBOM submissions from FY 2027-28 for vendors selling into Indian government and Critical Information Infrastructure. Organisations without a cryptographic inventory by then cannot produce one on demand.